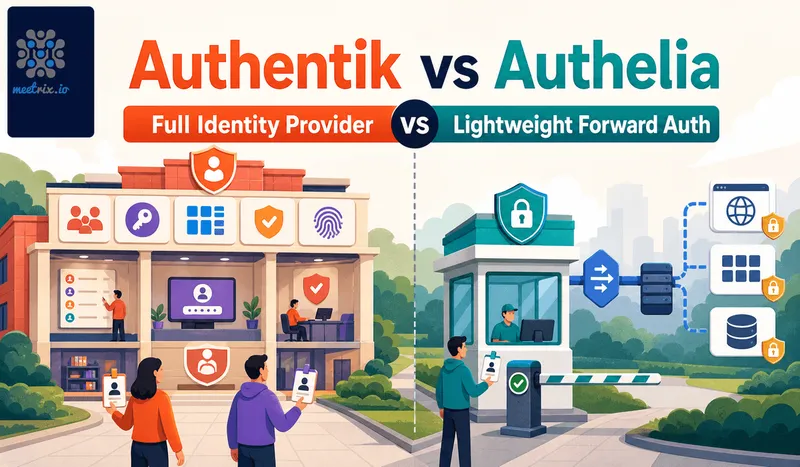
Authentik vs Authelia gets framed as a head-to-head more often than it should be. Authentik is a full identity provider: its own admin UI, user database, and support for OIDC, SAML, LDAP, and RADIUS. Authelia is forward-auth middleware that sits in front of a reverse proxy and decides whether a request needs a login before it's allowed through. They overlap at the edges, but picking between them starts with recognizing they're not really built to do the same job.
Quick answer
Jump to a section
Authentik: a full identity provider with an admin UI
Authentik's core is MIT licensed and built around a visual, flow-based configuration system with a proper web admin console for managing users, groups, applications, and access policies. Authentik proxy authentication works through outposts, lightweight proxy instances that can put SSO in front of an application with no native login support of its own, without modifying that application. Protocol coverage is broad: OIDC (with dynamic client registration), SAML, LDAP, RADIUS, and SCIM. An Enterprise tier at $5/user/month adds features like Google Workspace integration, WS-Federation, and mTLS login, mostly aimed at larger organizations.
Key features
- Full web admin UI for managing users, groups, and applications
- Outpost-based proxy that adds SSO to apps with zero native login support
- Broad protocol support: OIDC, SAML, LDAP, RADIUS, SCIM
- Visual, flow-based configuration for custom login and MFA sequences
Authelia: forward-auth middleware, not a full IdP
Authelia is Apache 2.0 licensed with roughly 25,000 GitHub stars, and its entire design is built around one job: sitting in front of a reverse proxy (Traefik, Nginx, Caddy, HAProxy) and deciding whether a request gets through or needs to authenticate first. There's no admin web UI by design, configuration lives in YAML files, which keeps the attack surface small and, per its own track record, has meant fewer reported vulnerabilities than tools that ship a full admin console. Fine-grained access rules match on subdomain, user, group, request path, method, and network, with a one-factor or two-factor policy chosen per rule. Since version 4.37, Authelia also ships an OIDC provider that has passed OpenID Foundation conformance certification, though the project itself still labels it beta, single sign-out isn't implemented yet.
Key features
- Forward-auth middleware for Traefik, Nginx, Caddy, and HAProxy
- No admin UI, configuration via YAML, smaller attack surface
- WebAuthn (FIDO2, passkeys) and TOTP two-factor authentication
- Fine-grained access rules by subdomain, user, group, path, and network
- OIDC provider since v4.37, OpenID certified, still beta with some gaps
Authelia vs Authentik: different categories of tool
This is the part worth being direct about. If your actual need is "give my team accounts and let them log into a dozen different self-hosted apps with one identity," Authentik is built for exactly that, and Authelia will feel like it's missing pieces because it was never trying to be that. If your actual need is "put a login wall in front of my Grafana, Portainer, and a few other dashboards that don't have their own auth," Authelia does that with less to run and less to secure, and Authentik will feel heavier than necessary. The "vs" framing makes sense for search intent, but the honest answer is closer to "which category of tool do you actually need," not "which one wins."
Resource footprint
Authelia can run as one container with SQLite for storage and sessions held in memory. Add Redis for sessions and PostgreSQL for storage once you run more than one instance, and it's three. Authentik needs three at minimum: a server process, a background worker, and PostgreSQL, plus outpost containers for each app you're proxying, and it idles at roughly 1GB of RAM. It used to need Redis as well, but release 2025.10 moved caching, tasks and sessions into PostgreSQL and dropped it; our Authentik high availability guide covers what that changes for a production setup. Neither is heavy by modern standards, but Authelia's footprint is noticeably lighter, which matters more on a small homelab server than it does on dedicated infrastructure.
Authentik SQLite: not an option
Short answer: no. Authentik needs PostgreSQL, and since 2025.10 that's the only thing it depends on. If a single-file database is the appeal, that's a point for Authelia.
Can you run both?
Yes, and some self-hosters do, for reasons that make sense once you see the category difference clearly. A common pattern: Authentik handles real identity, the apps that actually speak OIDC or SAML and need proper user accounts, while Authelia sits in front of the smaller dashboards and admin panels that have no login of their own and don't need a full identity record, just a login wall. It's not the default setup for most people, running one tool is simpler than running two, but it's a legitimate answer when your service list has both kinds of needs and you don't want to force everything through outposts just to gate a Portainer instance.
Authentik vs Authelia: feature comparison
| Feature | Authentik | Authelia |
|---|---|---|
| License | MIT (core) | Apache 2.0 |
| Category | Full identity provider | Forward-auth middleware |
| Admin web UI | Yes, full console | No, YAML configuration |
| Minimum stack | 3+ containers (server, worker, PostgreSQL) | 1 container on SQLite, 3 with Redis and PostgreSQL |
| Databases | PostgreSQL only | SQLite, PostgreSQL, MySQL |
| mTLS | mTLS login (Enterprise) | Can require client certificates on its own listener |
| SSO for apps with no native login | Yes, via outposts | Via reverse-proxy forward-auth |
| OIDC support | Comprehensive, dynamic client registration | Since v4.37, OpenID certified, still beta |
| SAML / LDAP / RADIUS | Yes | No |
| 2FA methods | Multiple, including WebAuthn | WebAuthn, TOTP |
Authelia vs Authentik vs Keycloak
Keycloak usually ends up on the same shortlist. It belongs in the same box as Authentik: a full identity provider, older, built on Java and heavier to run, and more at home in enterprise setups. So the real sequence is two decisions. First, if you need an IdP at all, Keycloak or Authentik (our Authentik vs Keycloak comparison covers that one). Second, whether you still want Authelia as a light login wall for the odd dashboard.
One newer option worth knowing about: Pocket ID, a small OIDC provider where users sign in with passkeys only. It's closer to Authelia in spirit than to Authentik, and worth a look if passwords are the thing you want gone.
Authentik vs Authelia isn't a contest either tool wins outright, they're built for adjacent but different jobs. Pick Authentik when you need a real identity provider with an admin UI and broad protocol support. Pick Authelia when a lightweight login wall in front of your reverse proxy is genuinely all you need, and you'd rather not run or secure a full admin console for that.
For the protocol details behind all of this, Authelia's proxy integration docs list every reverse proxy it supports. Our Authentik developer guide and single-click AWS setup guide cover the full identity provider path. If Authentik's protocol breadth feels like more than you need, our Keycloak developer guide covers the other full IdP we deploy, useful for comparison before you commit either way.
Frequently Asked Questions
Authentik vs Authelia: are they even solving the same problem?
Mostly not. Authentik is a full identity provider with its own admin UI, user database, and multi-protocol support. Authelia is forward-auth middleware that sits in front of a reverse proxy and decides whether a request needs a login first. They overlap at the edges, but Authelia isn't trying to be a drop-in Authentik replacement.
What is a good Authelia alternative with a full admin UI?
Authentik. Authelia has no web-based admin console by design, configuration is YAML files. If you want a UI for managing users, groups, and applications visually, Authentik is built for that; Authelia deliberately isn't.
What is a good lightweight sso self hosted option for a homelab?
Authelia, if you're already running a reverse proxy like Traefik, Nginx, or Caddy. It can run as a single container on SQLite (add Redis and PostgreSQL once you need more than one instance), where Authentik needs at least a server, a worker and PostgreSQL. It also has no admin UI to secure or maintain.
Does Authelia support authentik proxy authentication style SSO for apps without native login support?
Not the same way. Authentik's outposts can add SSO in front of an app with zero built-in authentication support of its own. Authelia's forward-auth model does something similar at the reverse-proxy layer, but it's configured through proxy rules and YAML, not Authentik's outpost system specifically.
Can Authelia act as a full OIDC identity provider?
Since version 4.37, yes, in a limited form. Authelia's OIDC provider has passed OpenID Foundation conformance certification, but the project itself still labels it beta, and features like single sign-out aren't implemented yet. Authentik's OIDC support is more complete.
Does Authentik support SQLite?
No. Authentik needs PostgreSQL. SQLite is an Authelia option, fine for a single-node homelab. Since release 2025.10 Authentik doesn't need Redis either, so PostgreSQL is its only external dependency.
Do Authelia and Authentik support mTLS?
In different ways. Authelia's server.tls.client_certificates setting makes Authelia itself require mutual TLS on its listener. Authentik offers mTLS as a login method, in its paid Enterprise tier.
Where does Keycloak fit in Authelia vs Authentik vs Keycloak?
Keycloak sits next to Authentik as a full identity provider, heavier and more enterprise-shaped. Authelia is still the odd one out: a login wall for a reverse proxy, not an IdP. Pick between Keycloak and Authentik first, then decide whether you need Authelia at all.
Which is more secure, Authentik or Authelia?
Authelia has historically reported fewer vulnerabilities, largely because it has a smaller attack surface: no admin UI, less code, and a single-purpose design. That's not a knock on Authentik's security, it's a natural consequence of Authentik doing more.
Launch Authentik on AWS in Minutes
Launch a pre-configured Authentik server on AWS, a full self-hosted identity provider with SSO already wired up.
Get Authentik on AWS Marketplace