Learn how to deploy Rancher on AWS with our step-by-step guide. It walks you through launching the Meetrix Rancher AMI with CloudFormation, pointing your domain at it, logging in for the first time, and keeping the server healthy once it runs.
Rancher is an open-source Kubernetes management platform from SUSE. From one dashboard you can create new clusters, import existing ones such as Amazon EKS, manage users and access, and deploy apps across all of them. The Meetrix image runs Rancher on a single EC2 instance on top of a lightweight K3s cluster, so you get a working management server in minutes instead of building one by hand. If you are running GPU workloads, our guides on GPU scheduling in Kubernetes and deploying vLLM on EKS pair well with a Rancher-managed cluster.
Prerequisites
Before you get started with the Rancher AMI, ensure you have the following prerequisites:
- Basic knowledge of AWS services, including EC2 instances and CloudFormation.
- An active AWS account with appropriate permissions.
- An EC2 key pair in the region you will deploy to.
- An S3 bucket in the same region for backups.
- If you encounter a vCPU quota error when launching the stack, follow https://meetrix.io/blogs/increase-aws-vcpu-quota/ to increase your vCPU limit.
Launching the AMI
Step 1: Find and Select Rancher AMI
- Log in to your AWS Management Console.
- Navigate to 'Rancher' in AWS Marketplace.
Step 2: Initial Setup & Configuration
- Click the "Continue to Subscribe" button.
- After subscribing, accept the terms and click "Accept Terms".
- Wait a few minutes until processing completes, then click "Continue to Configuration".
- Select "CloudFormation script to deploy Rancher" as the fulfillment option and choose your region. Click "Continue to Launch".
- From the "Choose Action" dropdown, select "Launch CloudFormation" and click "Launch".
Create CloudFormation Stack
Step 1: Create a stack
- Ensure the "Template is ready" option is selected under "Prepare template".
- Click "Next".
Step 2: Specify stack options
- Provide a unique "Stack name".
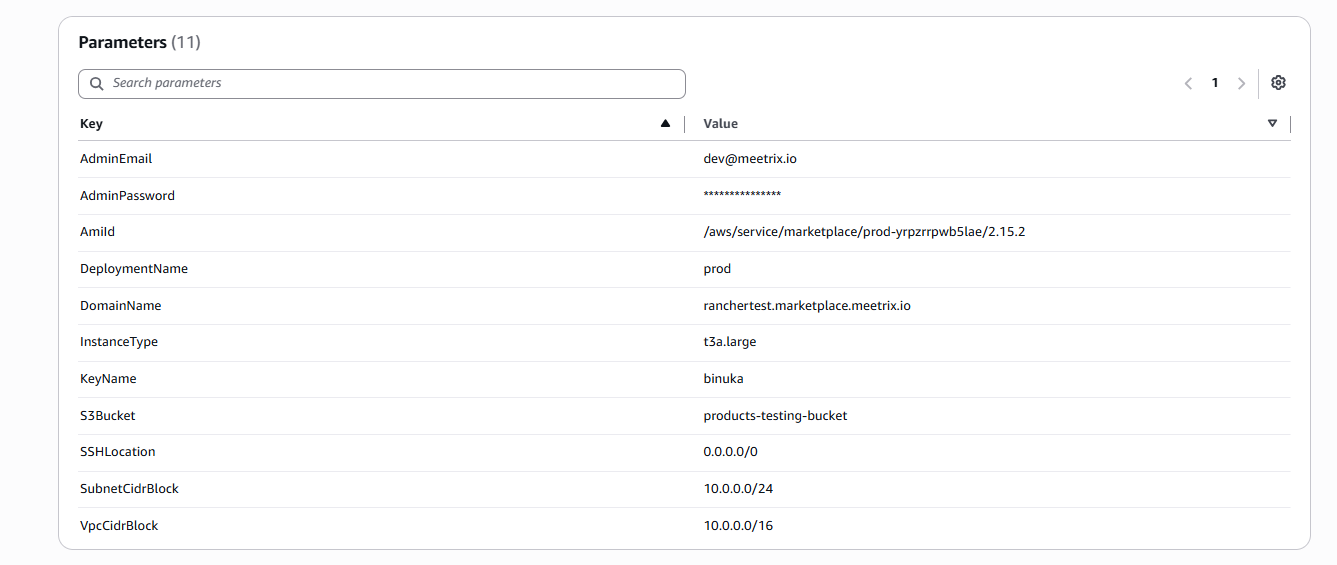
- Enter the "AdminEmail" used for SSL certificate generation.
- Enter an "AdminPassword". This is the bootstrap password you use for the first login to Rancher, so store it securely.
- Enter a value for "DeploymentName".
- Provide a public domain for "DomainName". Rancher will automatically try to set up SSL if the domain is hosted on Route 53. If unsuccessful, you must set up SSL manually.
- Choose an instance type "InstanceType" (Recommended: t3a.large).
- Select your preferred "KeyName".
- Enter the name of your S3 bucket for "S3Bucket", used for storing backups.
- Set "SSHLocation" to 0.0.0.0/0, or restrict it to your own IP range.
- Keep "SubnetCidrBlock" as 10.0.0.0/24.
- Keep "VpcCidrBlock" as 10.0.0.0/16.
- Click "Next".
Step 3: Configure stack options
- Choose "Roll back all stack resources" and "Delete all newly created resources" under "Stack failure options".
- Click "Next".
Step 4: Review
Review and verify the parameters you've entered.
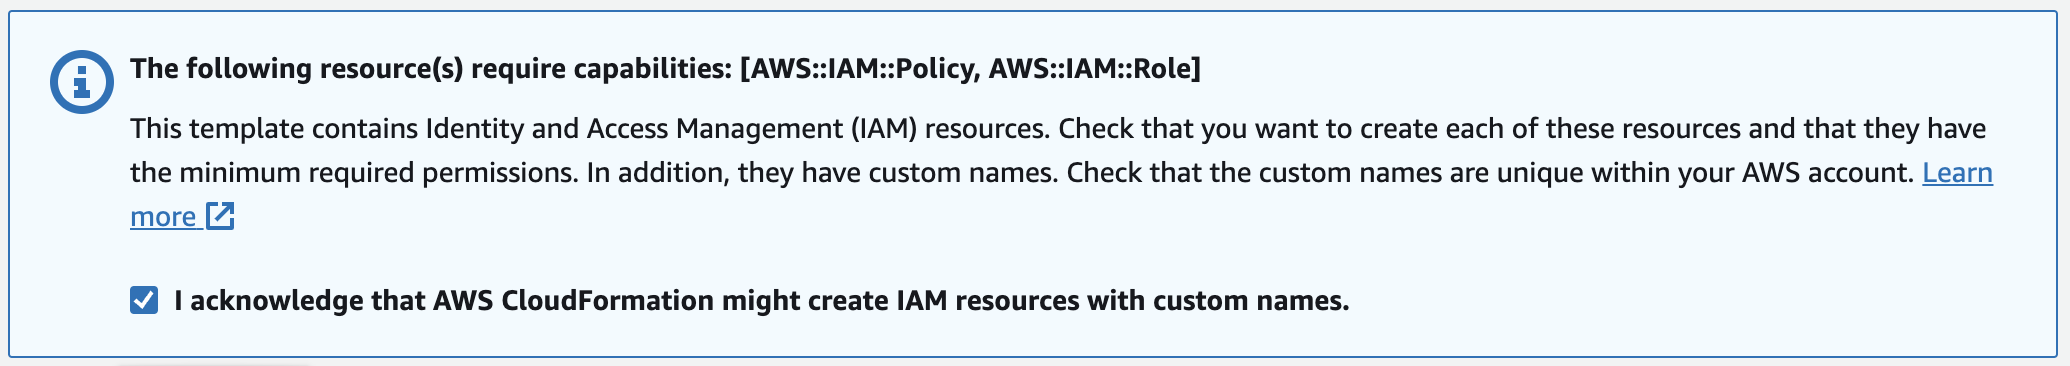
- Tick "I acknowledge that AWS CloudFormation might create IAM resources with custom names".
- Click "Submit".
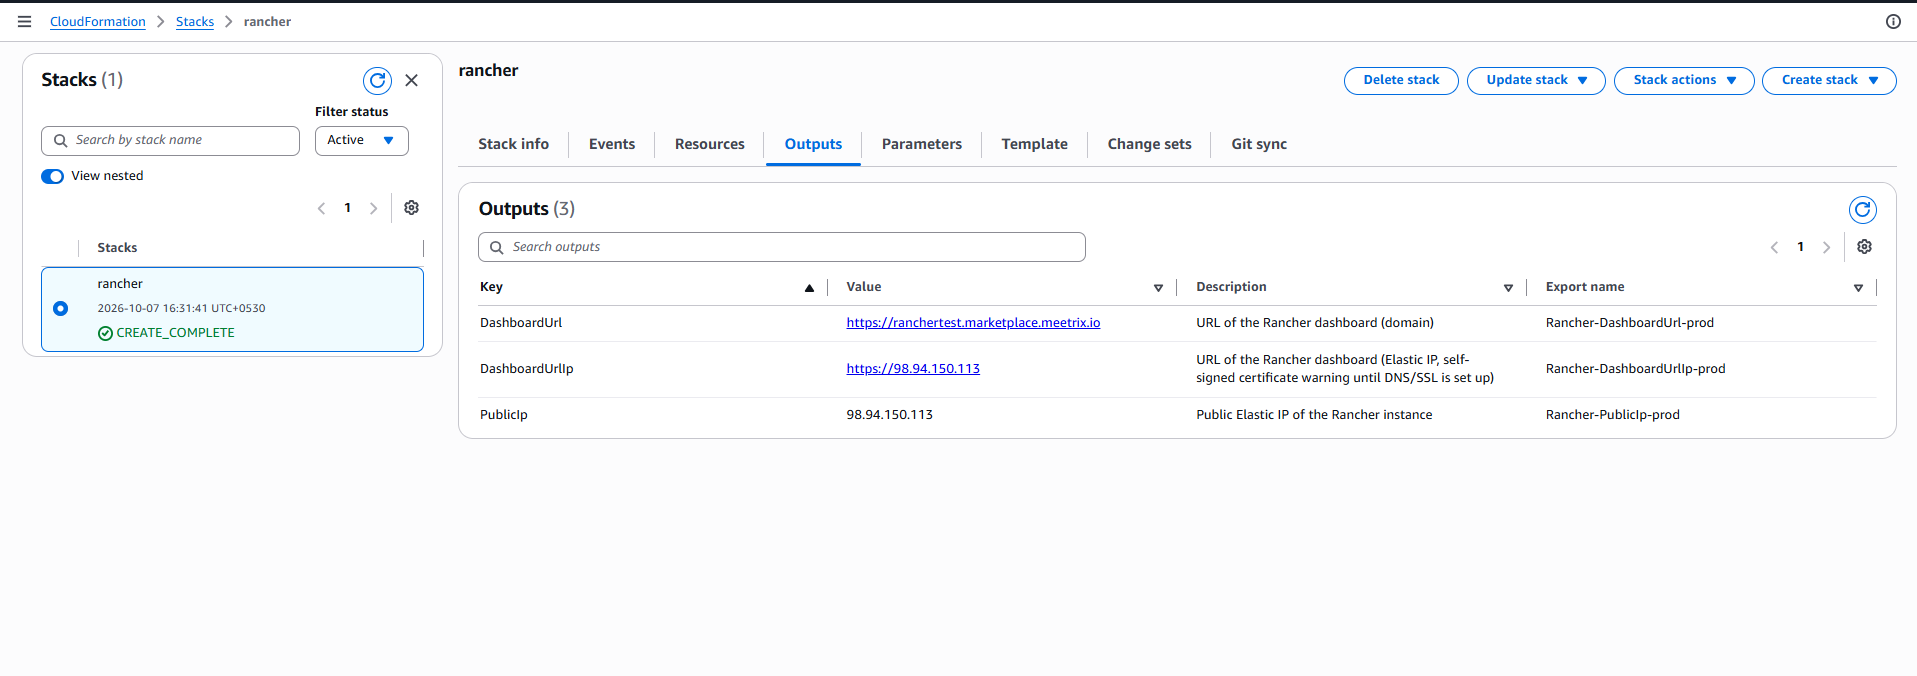
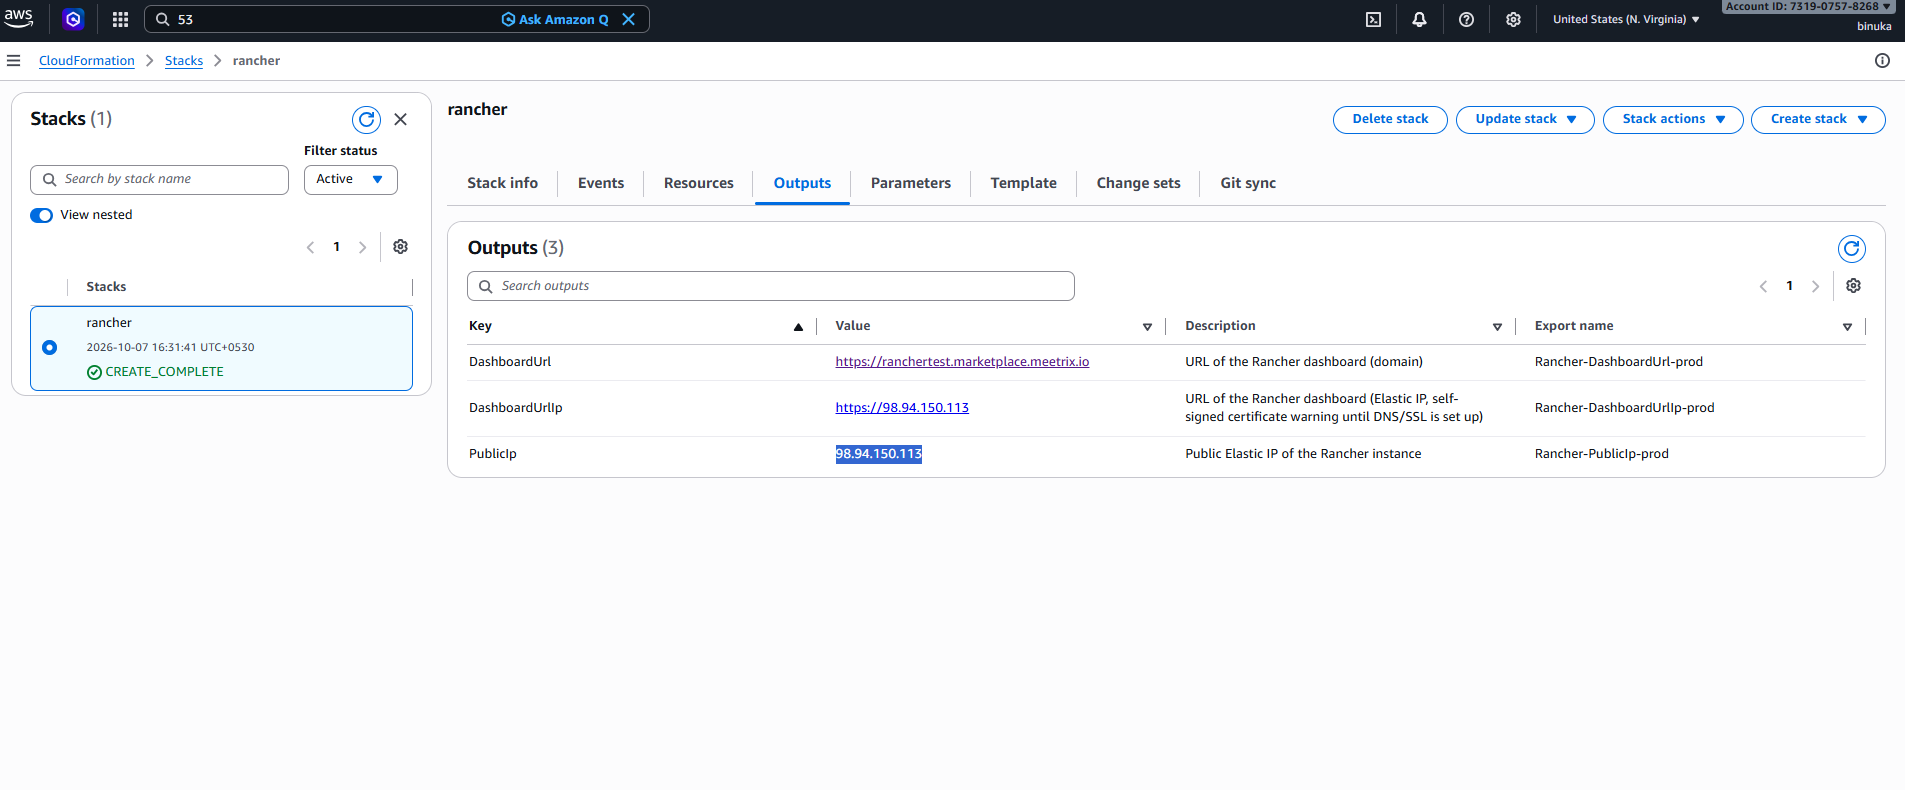
Afterward, you'll be directed to the CloudFormation stacks page. Please wait 5-10 minutes until the stack status shows CREATE_COMPLETE.
Update DNS
Step 1: Copy IP Address
Copy the public IP labeled "PublicIp" in the "Outputs" tab.
Step 2: Update DNS
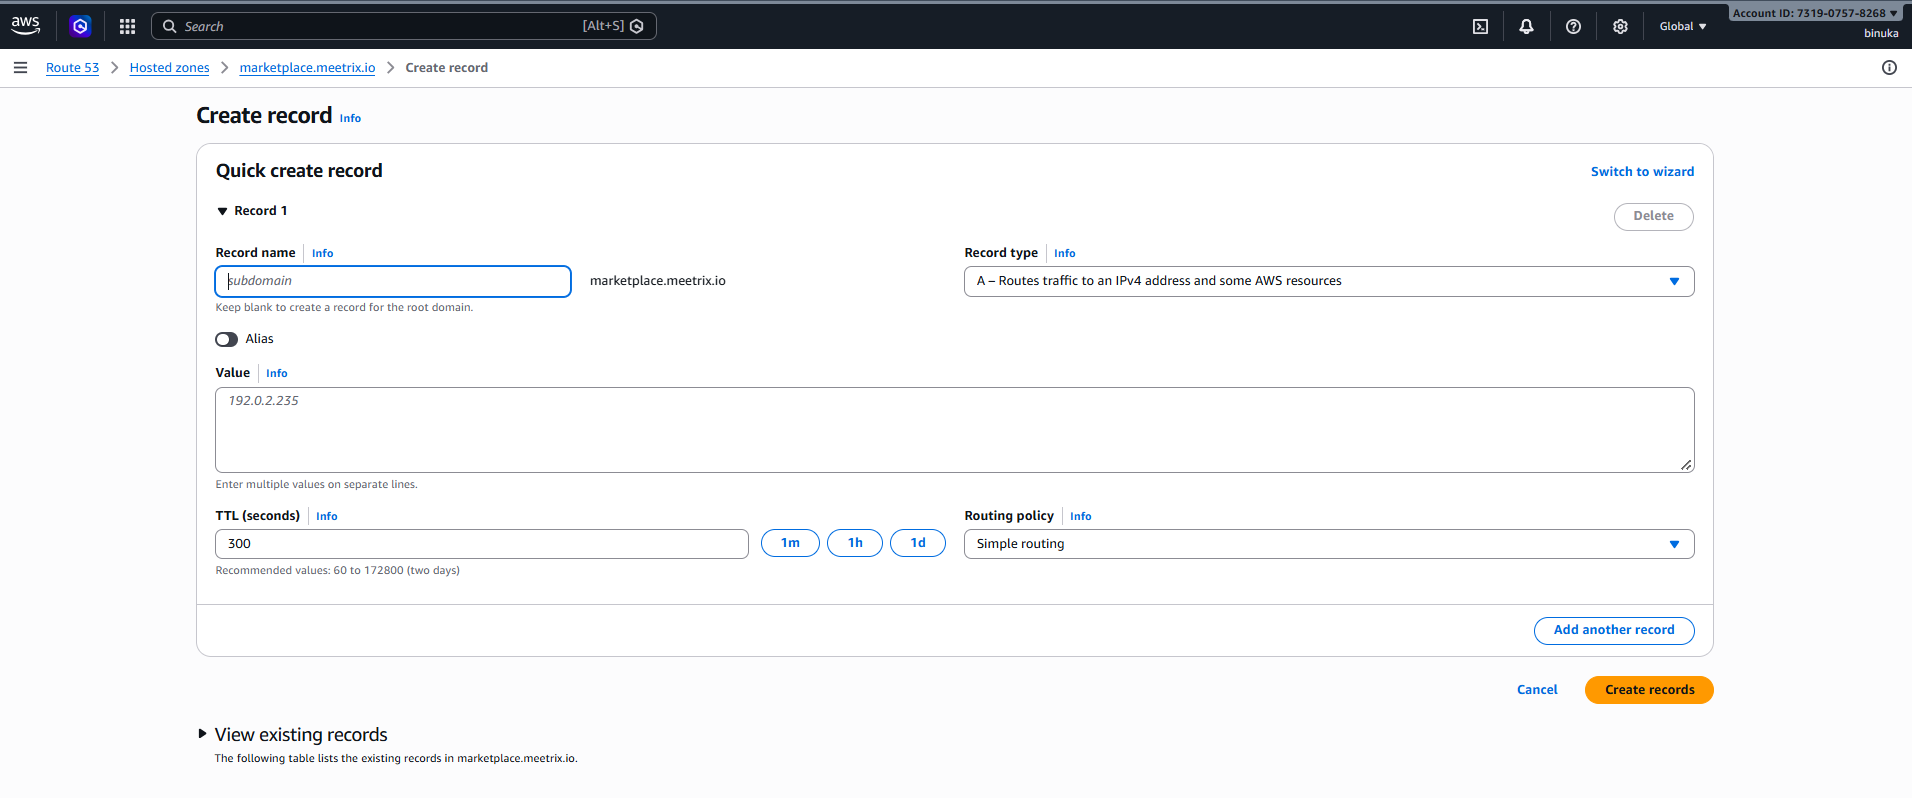
- Go to AWS Route 53 and navigate to "Hosted Zones".
- Click Create record.
- Add a record name matching the DomainName you entered, keep the record type as A, and paste the copied PublicIp into the value textbox.
- Click "Create records".
Access Rancher
Access Rancher using the "DashboardUrl" in the Outputs tab. Until DNS and SSL are in place you can use "DashboardUrlIp" instead, which shows a self-signed certificate warning in the browser.
Note
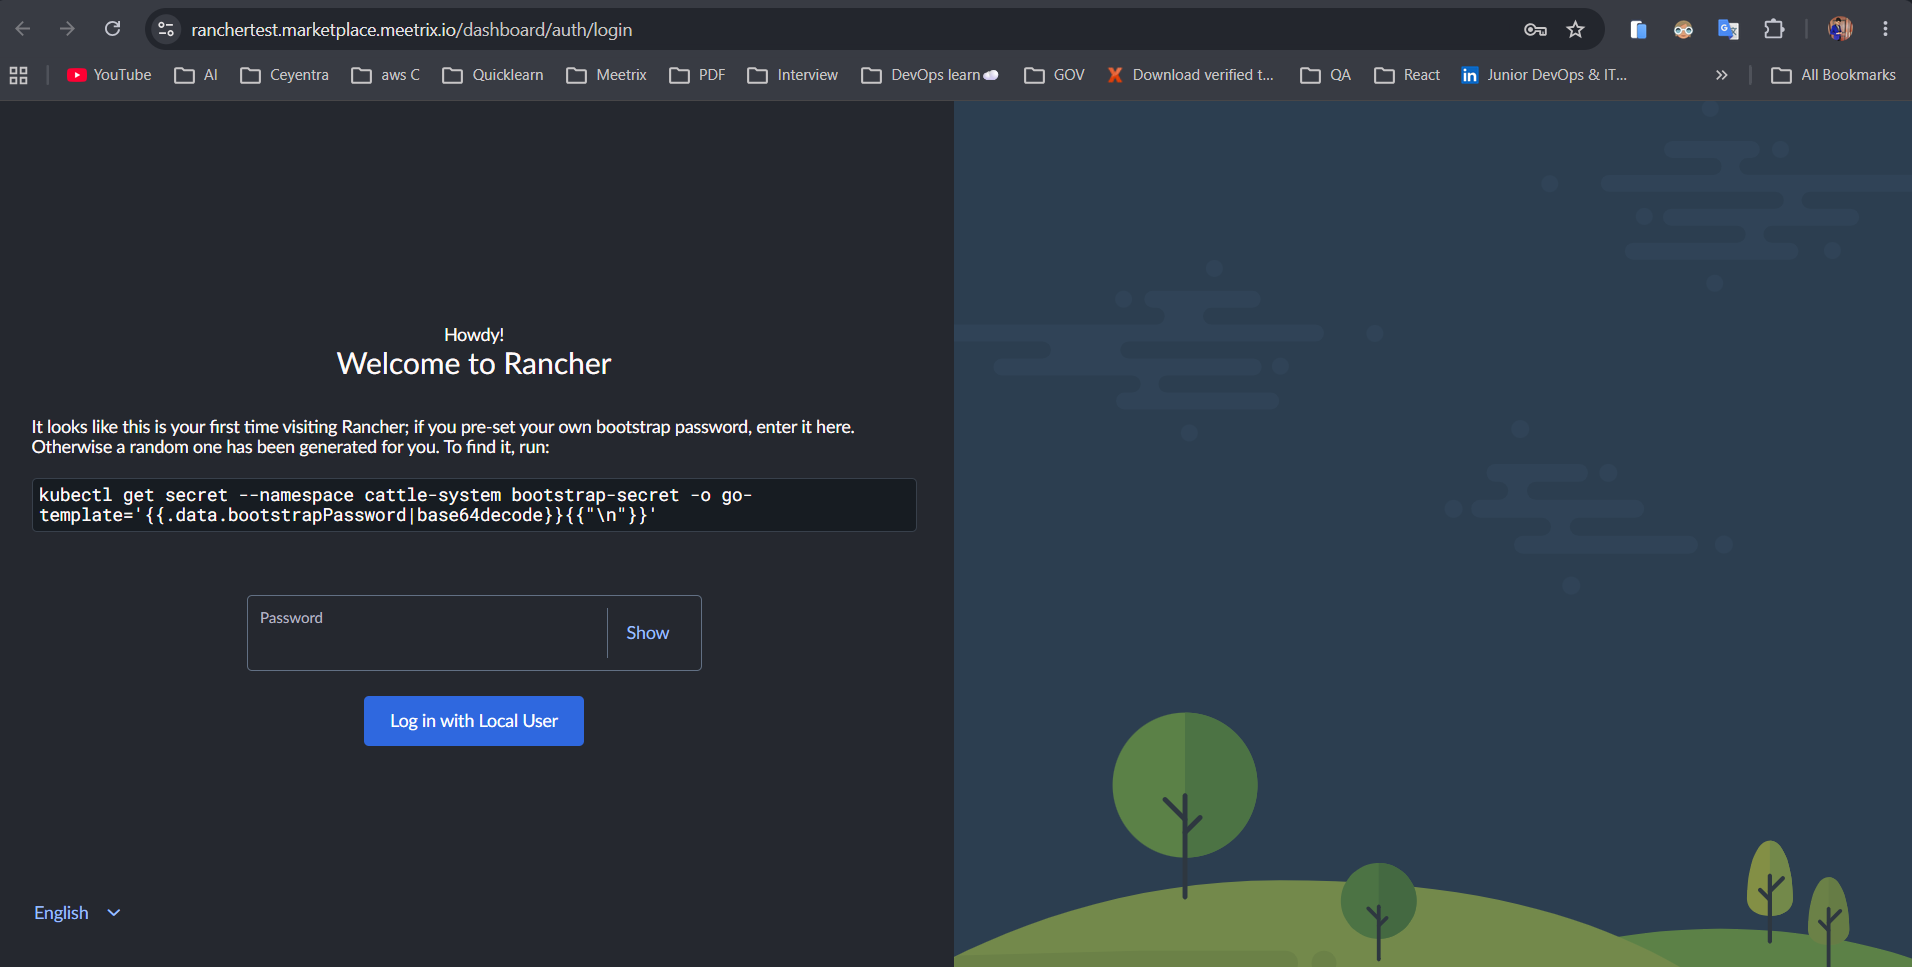
On the first visit, Rancher shows a "Welcome to Rancher" screen asking for a bootstrap password. Enter the AdminPassword you set in the stack parameters and click "Log in with Local User". You do not need to run the kubectl command shown on the screen.
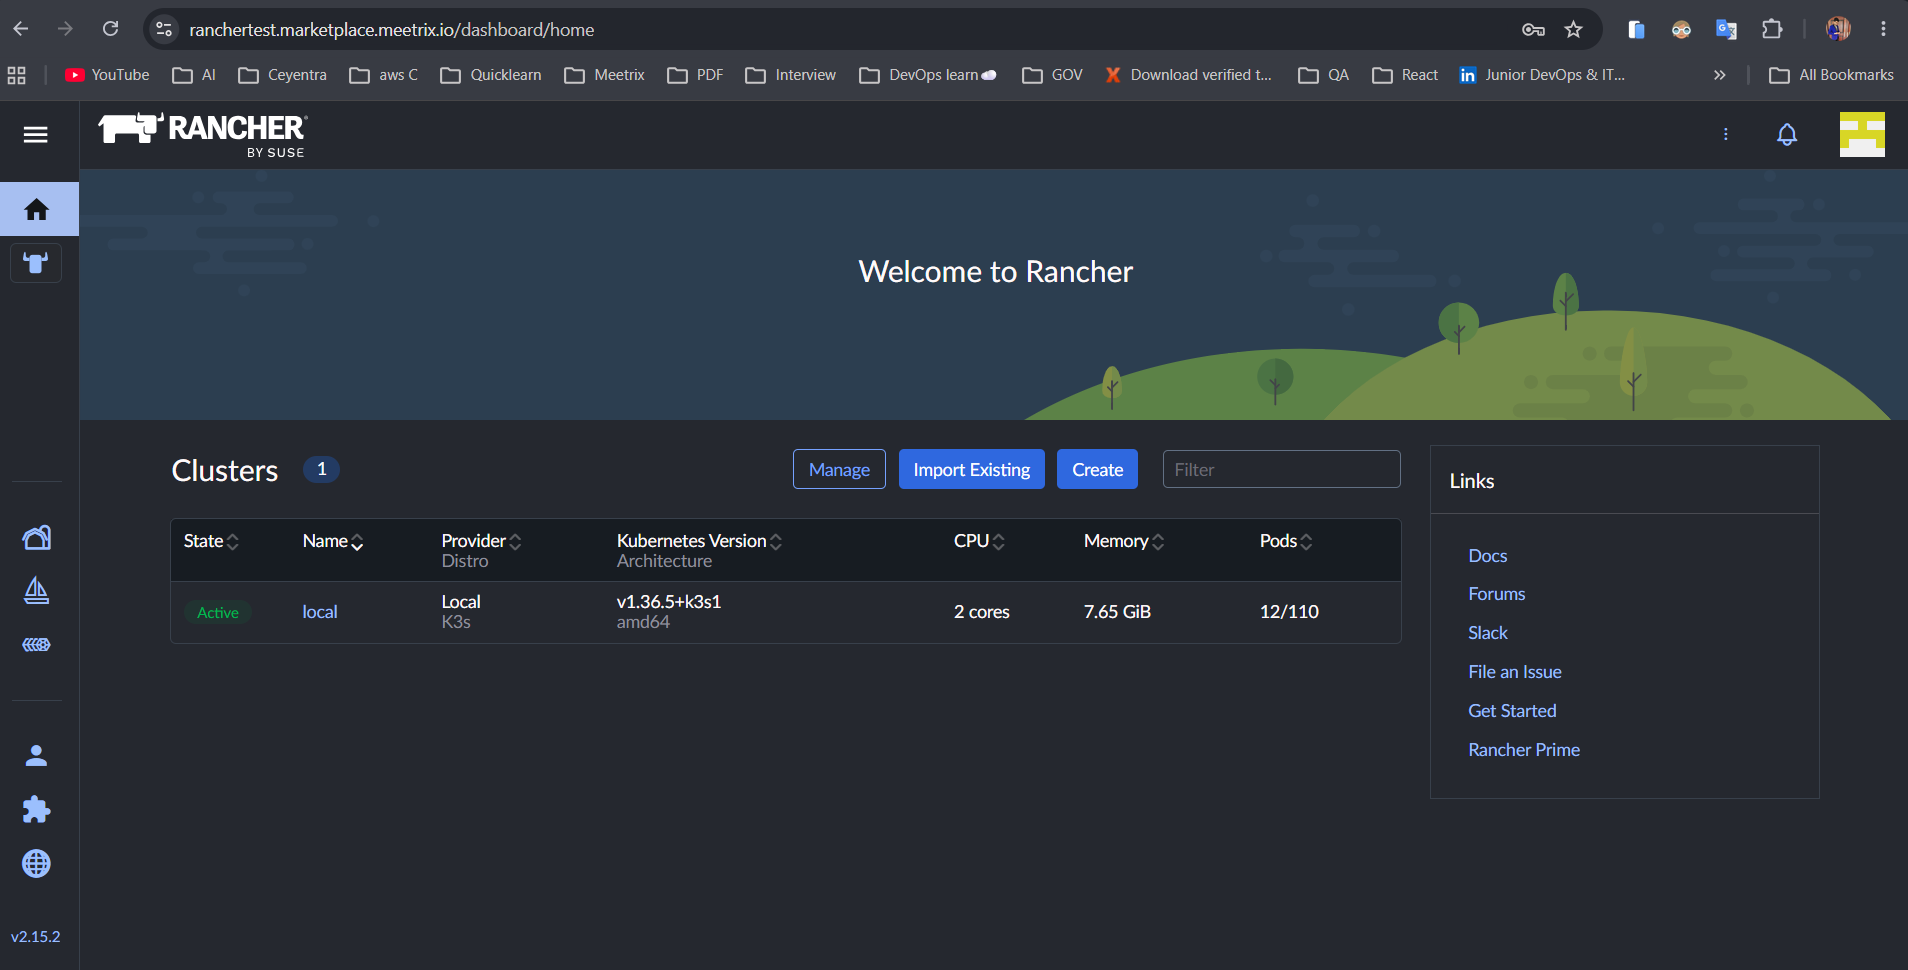
Follow the prompts to confirm the Server URL (your DashboardUrl) and accept the terms. You then land on the Rancher home page, where the local K3s cluster that Rancher runs on is already listed as Active. From here you can Create a new cluster or Import Existing ones. The Rancher documentation covers each cluster type in detail.
Generate SSL Manually
Rancher will automatically try to set up SSL when a Route 53-hosted domain is provided. If it fails, follow these steps to generate SSL manually.
Step 1: Copy IP Address
- Follow the Update DNS steps above, if not already done.
- Copy the Public IP indicated as "PublicIp" in the "Outputs" tab.
Step 2: Log in to the server
- Open the terminal and go to the directory where your private key is located.
- Run the following command, replacing the key name and IP address.
- Type "yes" and press Enter to confirm.
ssh -i <your key name> ubuntu@<Public IP address>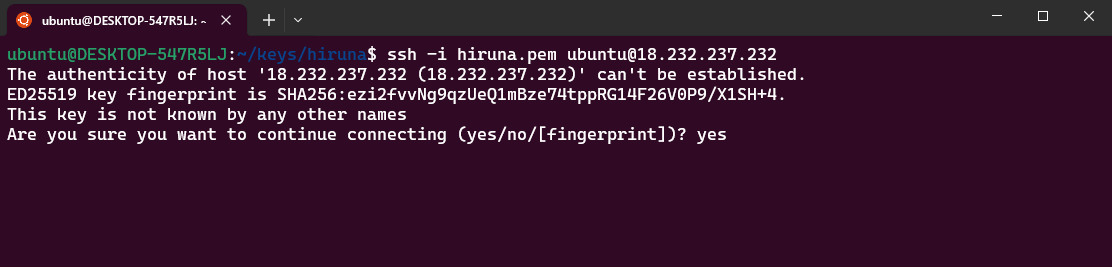
Step 3: Generate SSL
Run the following command and follow the prompts:
sudo /root/certificate_generate_standalone.shCheck Server Logs
Step 1: Log in to the server
ssh -i <your key name> ubuntu@<Public IP address>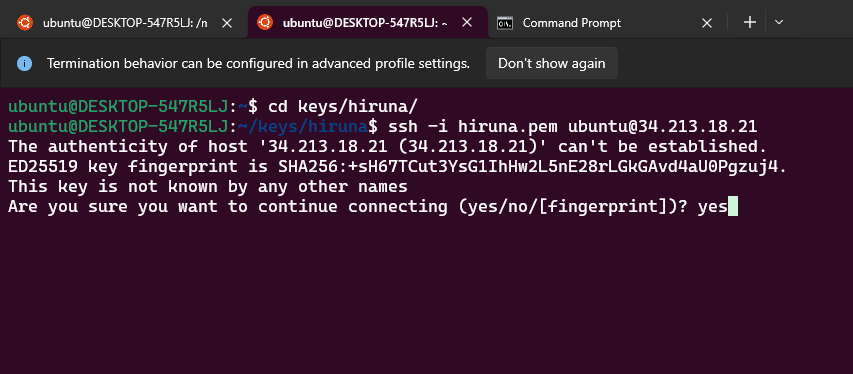
Step 2: Check the logs
List the running containers, then view the logs of the Rancher container using the first few characters of its container ID:
sudo docker ps

sudo docker logs <container-id-prefix>
Shutting Down Rancher
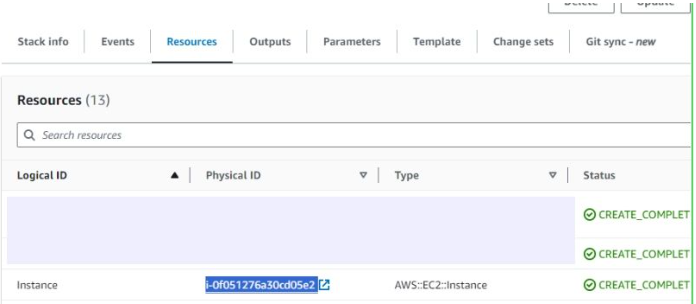
- In CloudFormation, click the link labeled "Instance" in the "Resources" tab to open the EC2 instance.
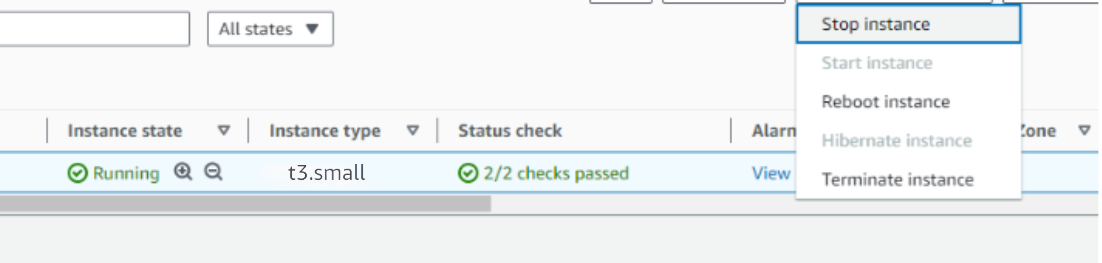
- Stop the Rancher instance from the Instance state dropdown. You can restart it later as needed.
Note
Remove Rancher
Delete the CloudFormation stack from the AWS Management Console under "CloudFormation Stacks" by clicking "Delete". Downstream clusters that Rancher created in your account are separate resources, so remove them first if you no longer need them.
Upgrades
When a new version is available in AWS Marketplace, remove the previous deployment after backing up necessary server data, and relaunch with the new version.
Troubleshoot
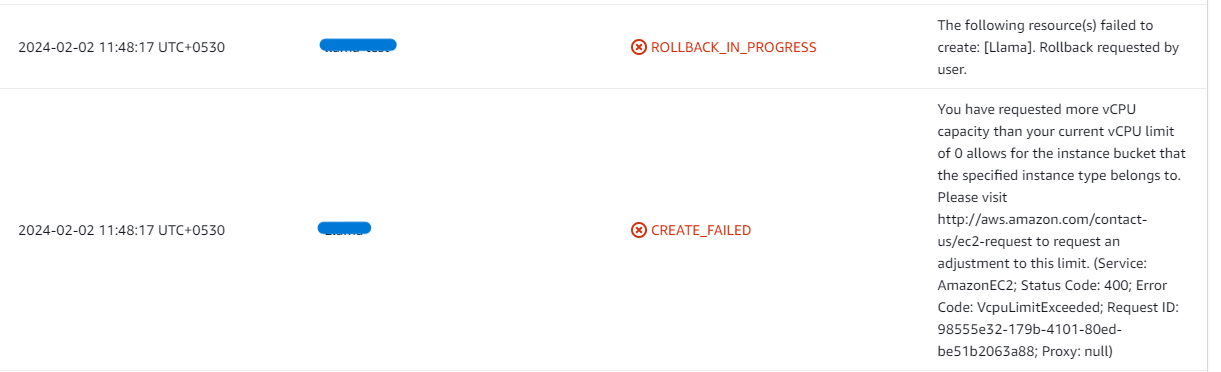
If you face vCPU quota limits, request an increase: How to increase AWS quota.
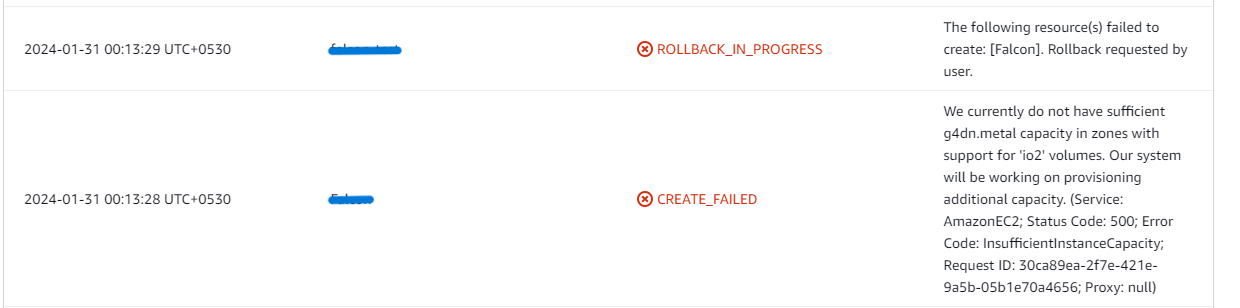
If you face insufficient capacity errors while creating the stack, try another region or time.
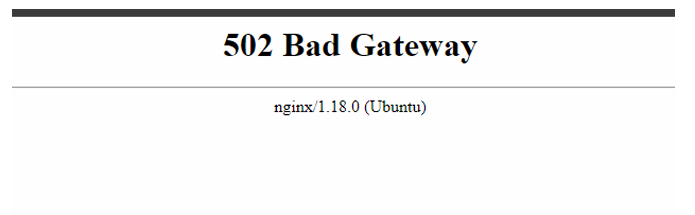
If the dashboard shows a 502 Bad Gateway error, wait 5-10 minutes and retry. Rancher can take a few minutes to start after the instance boots.
Check whether the instance storage is full. Log into the server and run:
df -h
If the root volume is between 90-100%, resize the EBS volume, then reboot and restart the service.
Conclusion
The Meetrix Rancher Deployment Guide helps you run a Kubernetes management server in your AWS environment. Whether you're a DevOps engineer, platform engineer, or IT leader, this guide provides step-by-step instructions for a secure setup. See the Rancher store page for what the Meetrix image includes and how it compares with OpenShift. If you want to monitor the clusters Rancher manages, our Grafana developer guide shows how to launch Grafana on AWS the same way.
Technical Support
Reach out to Meetrix Support (aws@meetrix.io) for assistance with Rancher issues.
Frequently Asked Questions
What is Rancher?
Rancher is an open-source Kubernetes management platform from SUSE. It gives you one web dashboard to create, import and operate Kubernetes clusters across clouds and on-premises, with central authentication, role-based access control, monitoring and app catalogs.
What is the initial password for the Rancher dashboard?
The first login screen asks for a bootstrap password. Enter the AdminPassword you set in the CloudFormation stack parameters. Rancher then asks you to confirm the server URL and agree to the terms before opening the dashboard.
What is the local cluster shown on the Rancher home page?
The local cluster is the K3s cluster that Rancher itself runs on, on the same EC2 instance. Keep it for running Rancher and create or import separate clusters for your workloads.
Which instance type is recommended?
t3a.large (2 vCPU, 8 GiB memory) is the recommended baseline. Choose a larger instance if Rancher will manage many downstream clusters or nodes.
What is the S3Bucket parameter used for?
It is an S3 bucket in your account that the instance uses to store backups. Create the bucket before launching the stack, in the same region.
How do I upgrade Rancher?
When a new version is available in AWS Marketplace, back up the data you need, remove the previous deployment, then launch a new stack with the new version.
How do I get technical support?
Reach out to Meetrix Support at aws@meetrix.io for assistance with Rancher issues.
Ready to Deploy Your Own Rancher Server?
Get started in minutes with our pre-configured AMI and manage all your Kubernetes clusters from one dashboard.
Deploy Rancher from AWS Marketplace