Learn how to install and configure Zulip on AWS with our step-by-step deployment guide. This resource walks you through provisioning your cloud environment, deploying Zulip securely, creating your first organization, and operating it reliably in a self-hosted AWS environment. Whether you're moving your team off a hosted chat subscription or want your conversations to stay inside your own AWS account, this guide will help you set up and run Zulip efficiently in the cloud.
Zulip takes a different approach from most team chat tools. Every message belongs to a channel and a topic, so conversations stay threaded and easy to catch up on. If you are still weighing your options, our Rocket.Chat vs Mattermost comparison and Mattermost vs Slack breakdown cover the other popular self-hosted choices. Let's get started deploying Zulip on AWS.
Prerequisites
Before you get started with the Zulip AMI, ensure you have the following prerequisites:
- Basic knowledge of AWS services, including EC2 instances and CloudFormation.
- An active AWS account with appropriate permissions.
- SMTP credentials (host, port, username and password) so Zulip can send sign-up and invitation emails.
- If you encounter a vCPU quota error when launching the stack, follow https://meetrix.io/blogs/increase-aws-vcpu-quota/ to increase your vCPU limit.
Launching the AMI
Step 1: Find and Select the Zulip AMI
- Log in to your AWS Management Console.
- Navigate to 'Zulip' in AWS Marketplace.
Step 2: Initial Setup & Configuration
- Click the "Continue to Subscribe" button.
- After subscribing, accept the terms and click "Accept Terms".
- Wait a few minutes until processing completes, then click "Continue to Configuration".
- Select "CloudFormation script to deploy Zulip" as the fulfillment option and choose your region. Click "Continue to Launch".
- From the "Choose Action" dropdown, select "Launch CloudFormation" and click "Launch".
Create CloudFormation Stack
Step 1: Create a stack
- Ensure the "Template is ready" option is selected under "Prepare template".
- Click "Next".
Step 2: Specify stack options
- Provide a unique "Stack name".
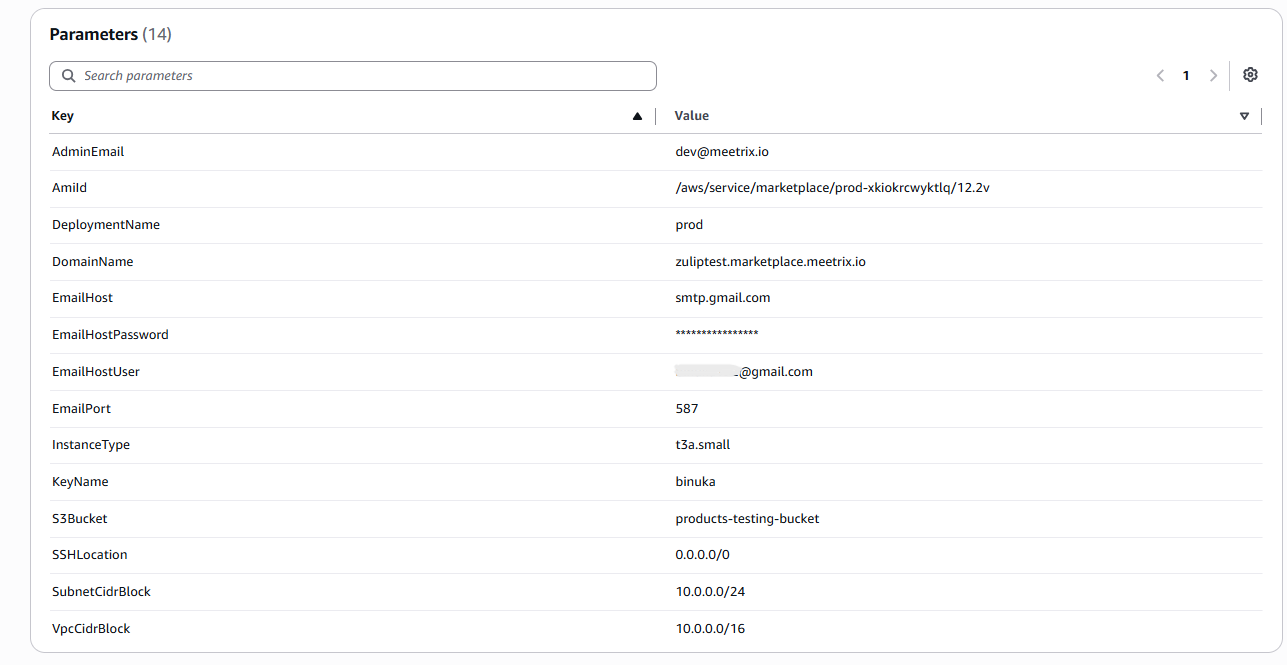
- Enter the "AdminEmail" used for SSL certificate generation.
- Enter a value for "DeploymentName".
- Provide a public domain for "DomainName". Zulip will automatically try to set up SSL if the domain is hosted on Route53. If unsuccessful, you must set up SSL manually.
- Enter your SMTP server for "EmailHost" (for example, smtp.gmail.com).
- Enter the SMTP password for "EmailHostPassword". For Gmail, use an app password rather than your account password.
- Enter the SMTP username for "EmailHostUser", usually the full sending email address.
- Enter the SMTP port for "EmailPort" (587 for STARTTLS).
- Choose an instance type "InstanceType" (Recommended: t3a.small for small teams, larger as usage grows).
- Select your preferred "KeyName".
- Provide an S3 bucket name for "S3Bucket", used for storing backups.
- Set "SSHLocation" to 0.0.0.0/0.
- Keep "SubnetCidrBlock" as 10.0.0.0/24.
- Keep "VpcCidrBlock" as 10.0.0.0/16.
- Click "Next".
Step 3: Configure stack options
- Choose "Roll back all stack resources" and "Delete all newly created resources" under "Stack failure options".
- Click "Next".
Step 4: Review
Review and verify the details you've entered. Here's an example of a completed set of stack parameters:
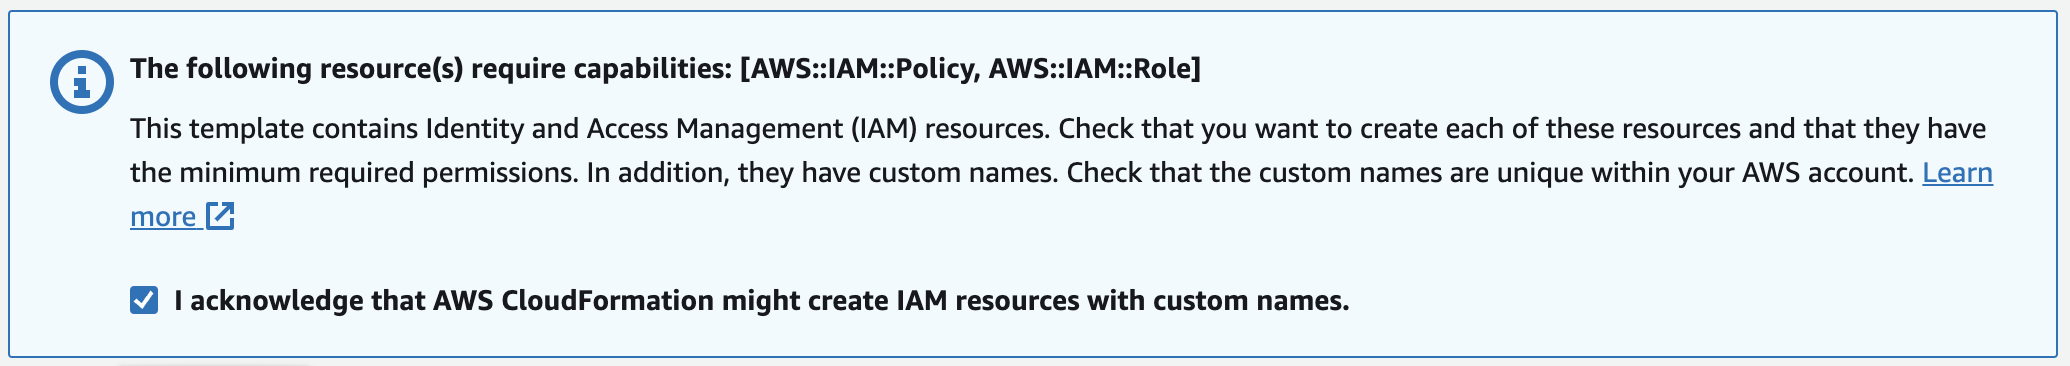
- Tick "I acknowledge that AWS CloudFormation might create IAM resources with custom names".
- Click "Submit".
Afterward, you'll be directed to the CloudFormation stacks page. Please wait for 5-10 minutes until the stack has been successfully created.
Update DNS
Step 1: Copy IP Address
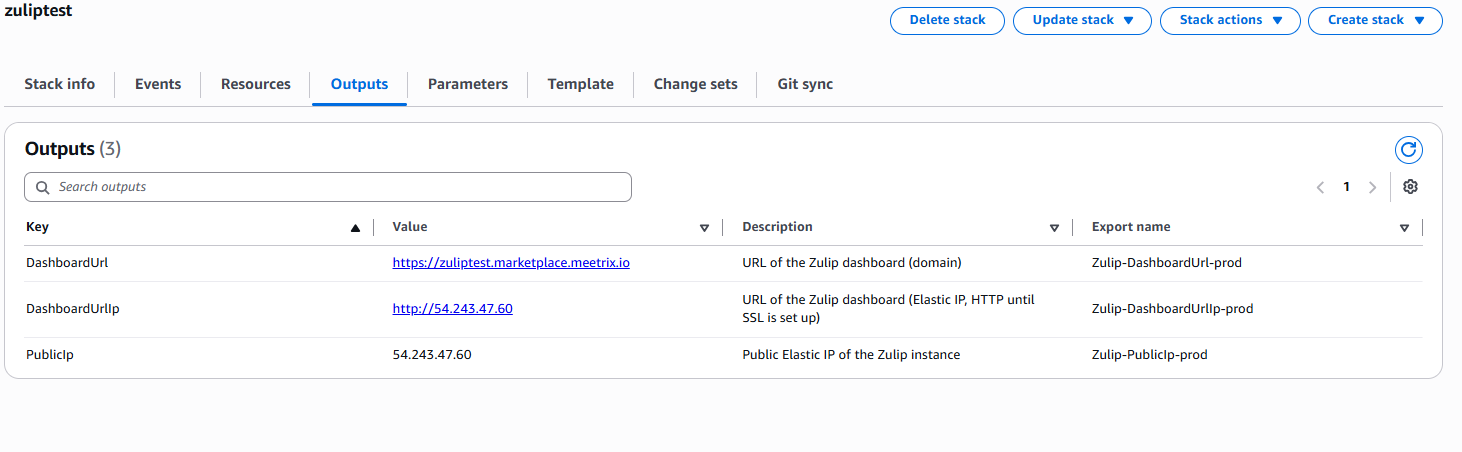
Copy the public IP labeled "PublicIp" in the "Outputs" tab.
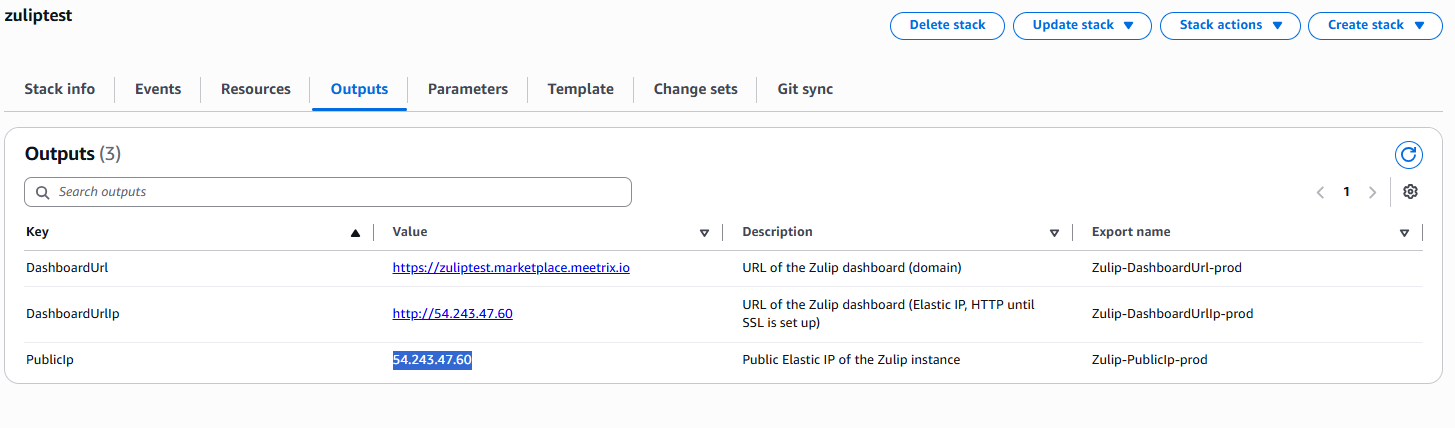
Step 2: Update DNS
- Go to AWS Route 53 and navigate to "Hosted Zones".
- Click Create record.
- Add a record name and paste the copied PublicIp into the value textbox.
- Click "Save".
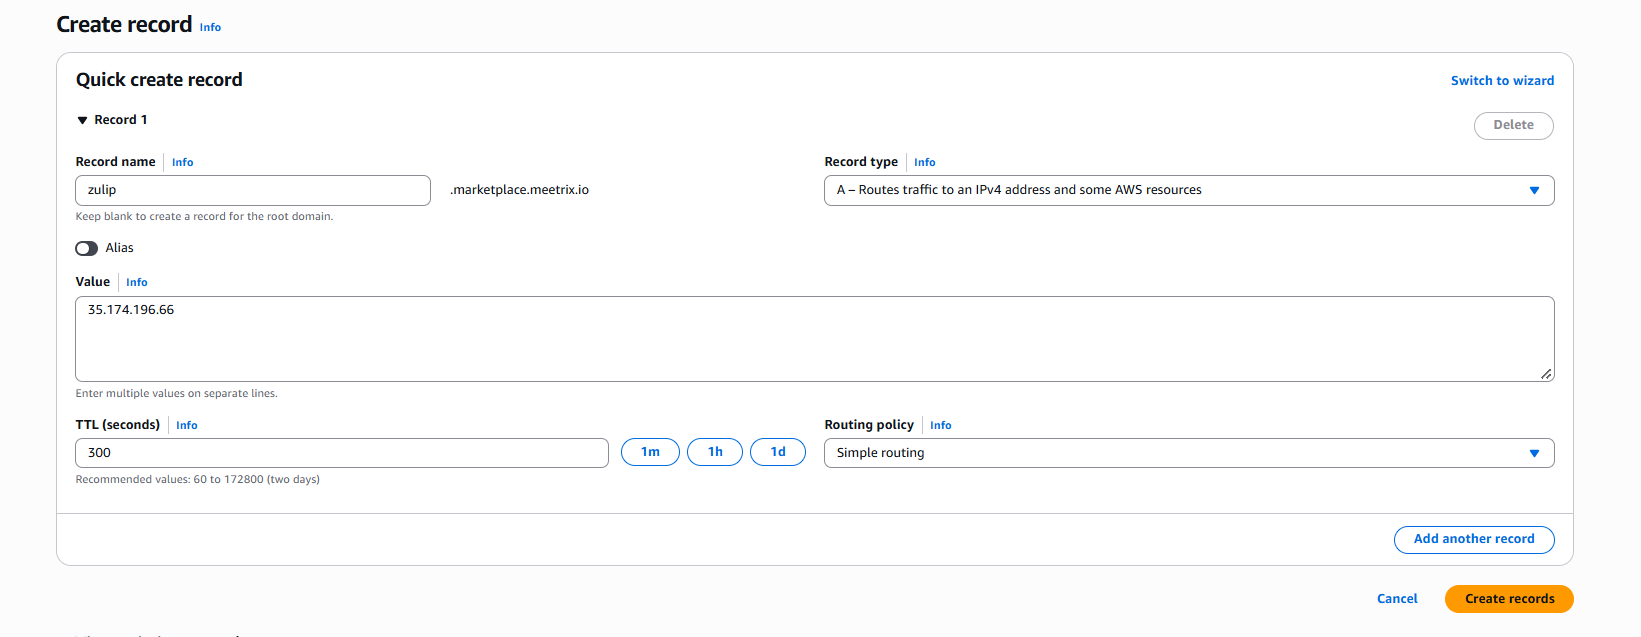
Access Zulip
Access Zulip using the "DashboardUrl" or "DashboardUrlIp" provided in the Outputs tab.
Note
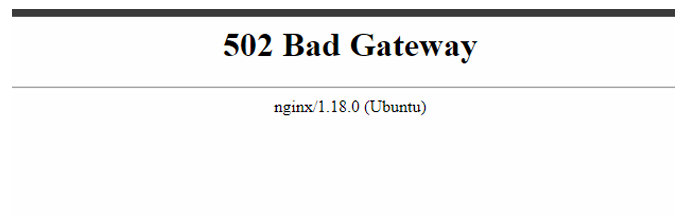
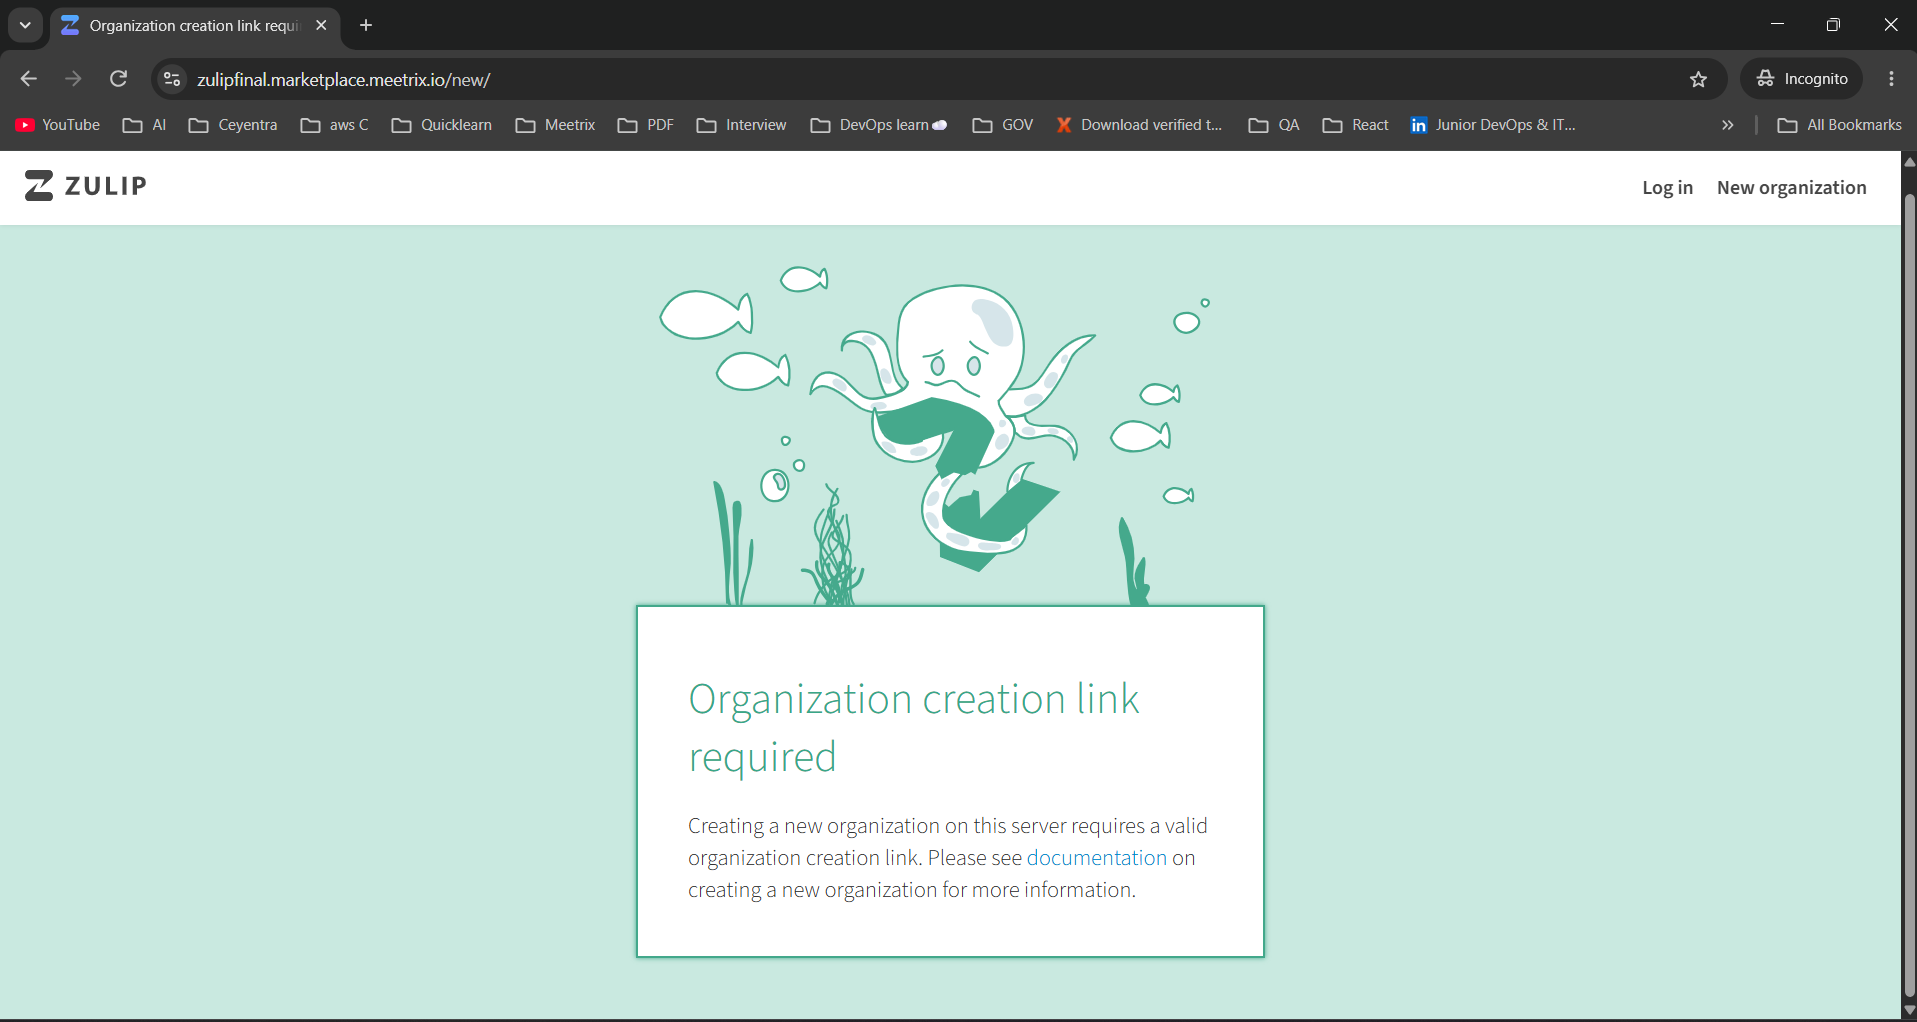
A fresh Zulip server has no organization yet, so the first page you see is "No organization found". This is expected.
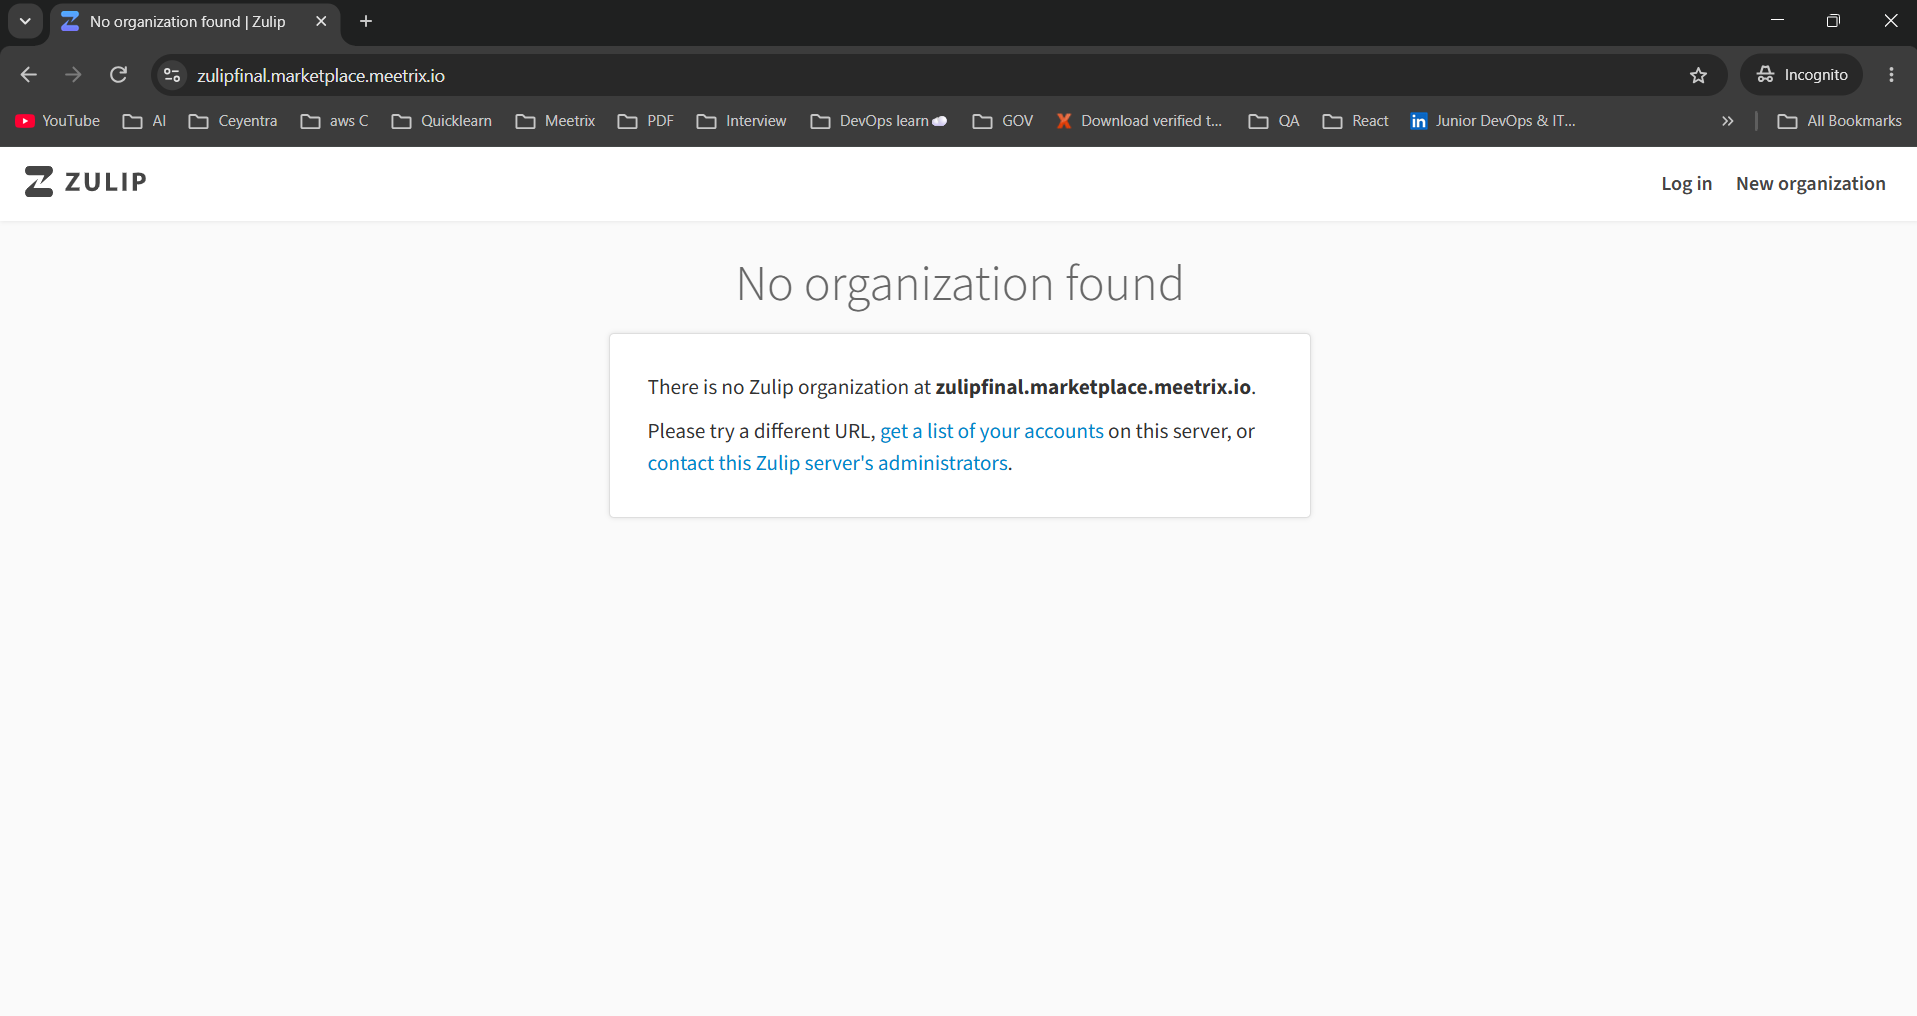
Clicking "New organization" will not help yet either. Zulip requires a secure, single-use link before anyone can create an organization on the server.
Step 1: Log in to the server
- Open the terminal and go to the directory where your private key is located.
- Run the SSH command below.
- Type "yes" and press Enter to confirm.
ssh -i <your key name> ubuntu@<Public IP address>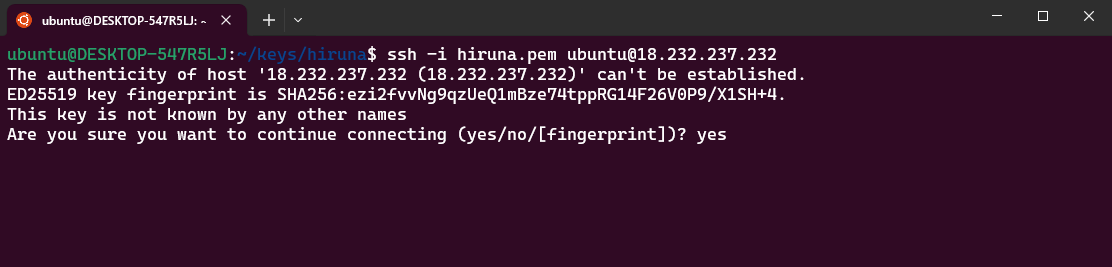
Step 2: Generate an organization creation link
Run Zulip's management command to generate the link:
sudo -u zulip /home/zulip/deployments/current/manage.py generate_realm_creation_link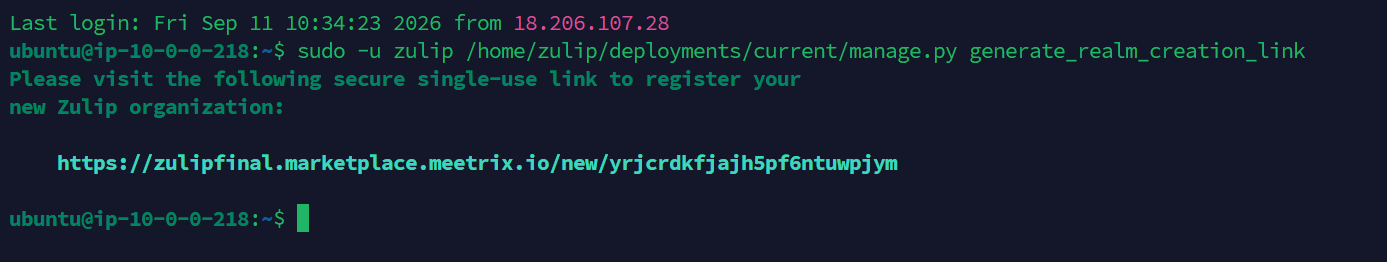
Step 3: Create your organization
Open the link in your browser. Enter the Organization name, choose the Organization type and language, enter your email, and click "Create organization". Zulip sends a confirmation email to finish creating your admin account, which is why the SMTP parameters need to be correct.
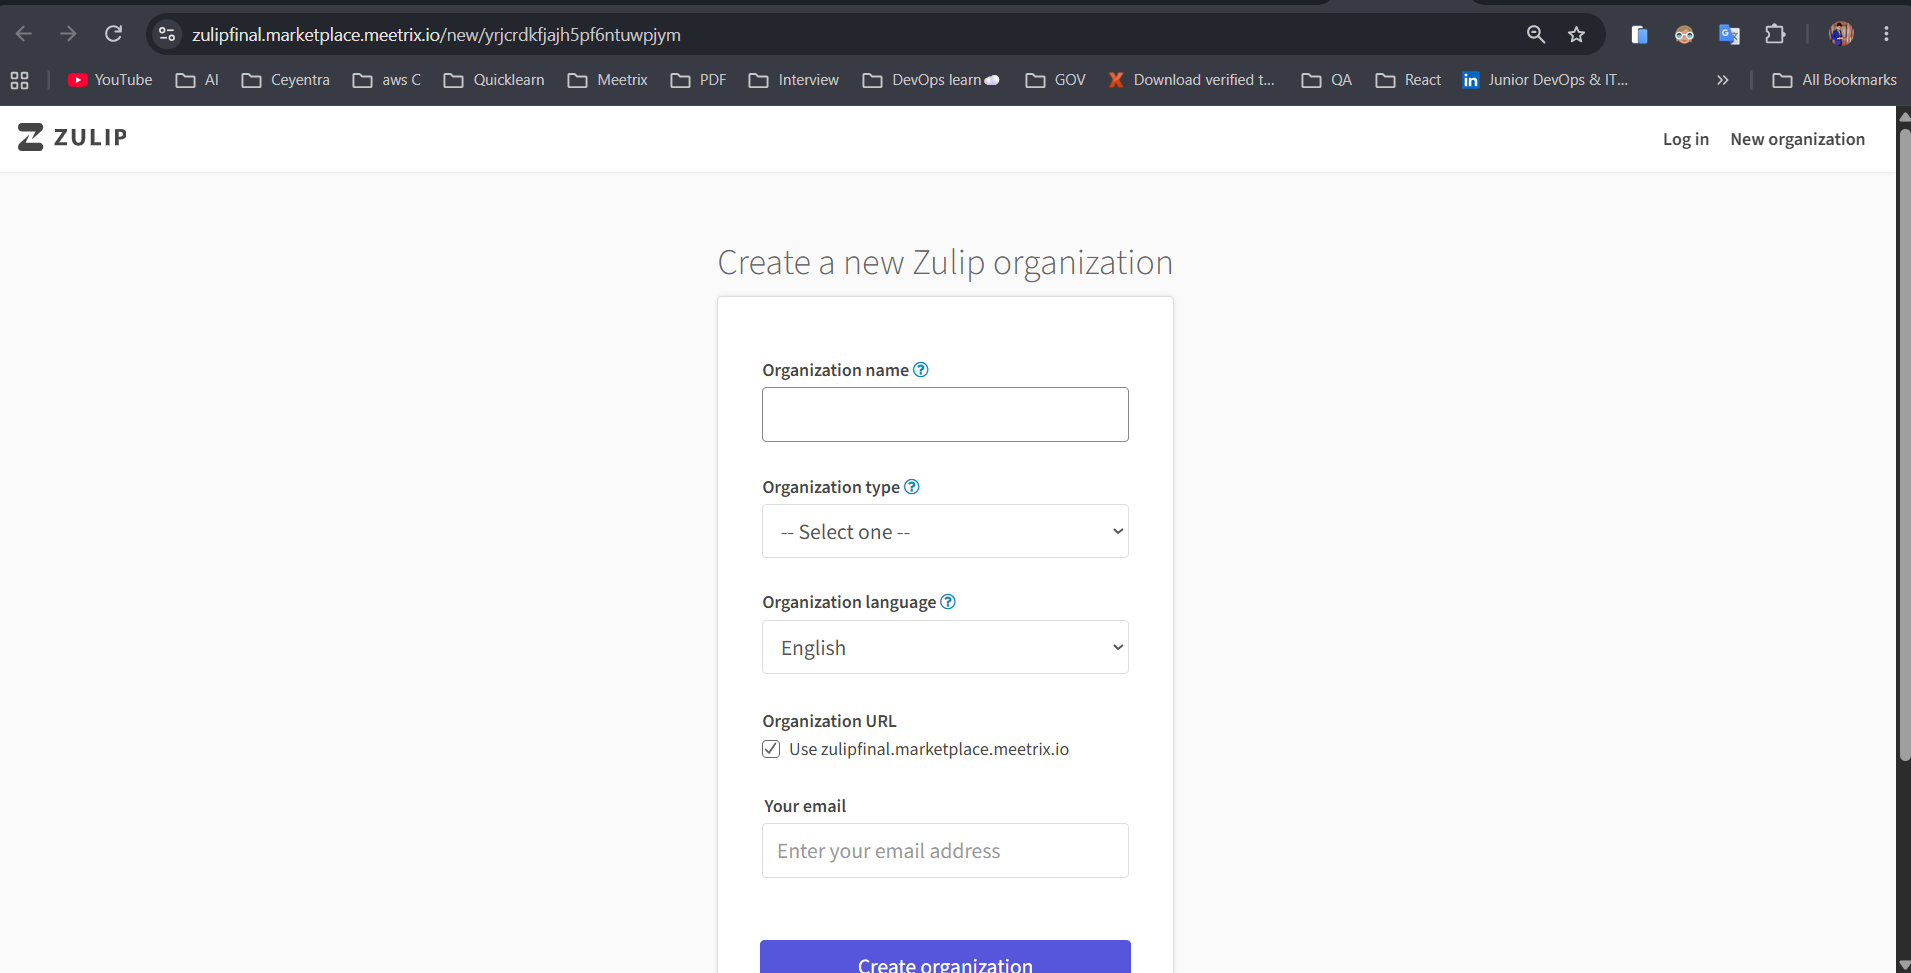
The link works once. If you need another organization or the link expires, run the command again. If your team already uses a central identity provider, Zulip also supports SAML and OpenID Connect login - our Authentik developer guide shows how to run one on AWS.
Generate SSL Manually
Zulip will automatically try to set up SSL when a Route53-hosted domain is provided. If it fails, follow these steps to generate SSL manually.
Step 1: Copy IP Address
Follow the Update DNS steps above, if not already done, and copy the Public IP indicated as "PublicIp" in the "Outputs" tab.
Step 2: Log in to the server
ssh -i <your key name> ubuntu@<Public IP address>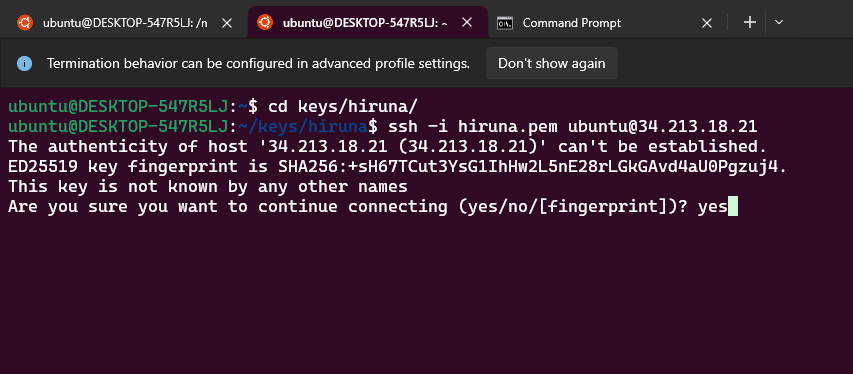
Step 3: Generate SSL
Run Zulip's certbot setup script, replacing the admin email and domain with your own:
sudo /home/zulip/deployments/current/scripts/setup/setup-certbot --email=<admin-email> --agree-tos <your-domain>Check Server Logs
Step 1: Log in to the server
ssh -i <your key name> ubuntu@<Public IP address>Step 2: Check the logs
Check that Zulip's services are running, then read the server and error logs:
sudo supervisorctl status

sudo tail -n 100 /var/log/zulip/server.log

sudo tail -n 100 /var/log/zulip/errors.log
Shutting Down Zulip
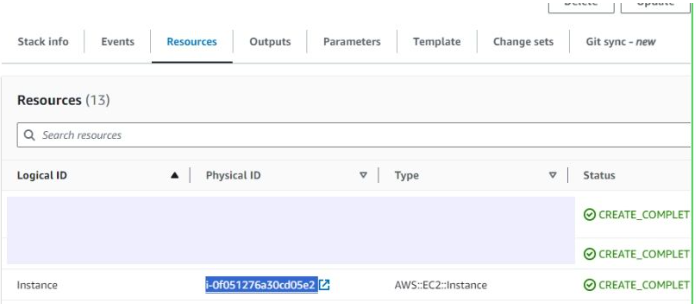
- In CloudFormation, click the link labeled "Instance" in the "Resources" tab to open the EC2 instance.
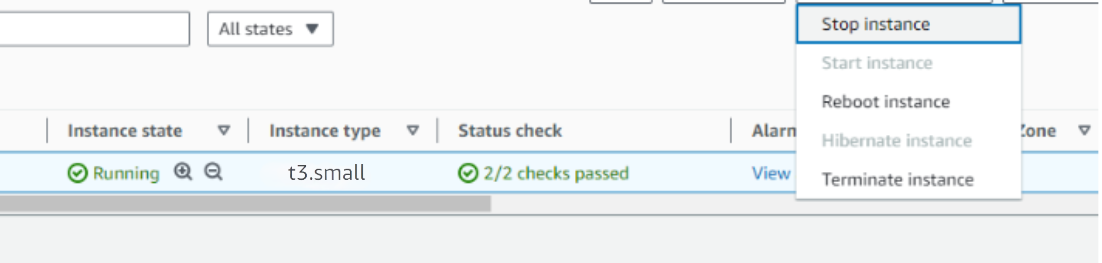
- Stop the Zulip instance from the Instance state dropdown. You can restart it later as needed.
Remove Zulip
Delete the CloudFormation stack from the AWS Management Console under "CloudFormation Stacks" by clicking "Delete".
Upgrades
When a new version is available in AWS Marketplace, remove the previous deployment after backing up necessary server data, and relaunch with the new version.
Troubleshoot
- If you face vCPU quota limits, request an increase: How to increase AWS quota.
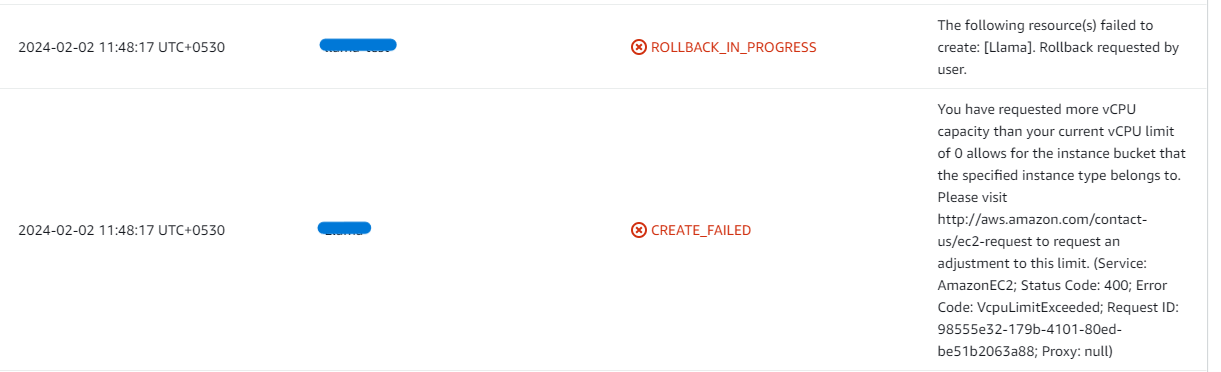
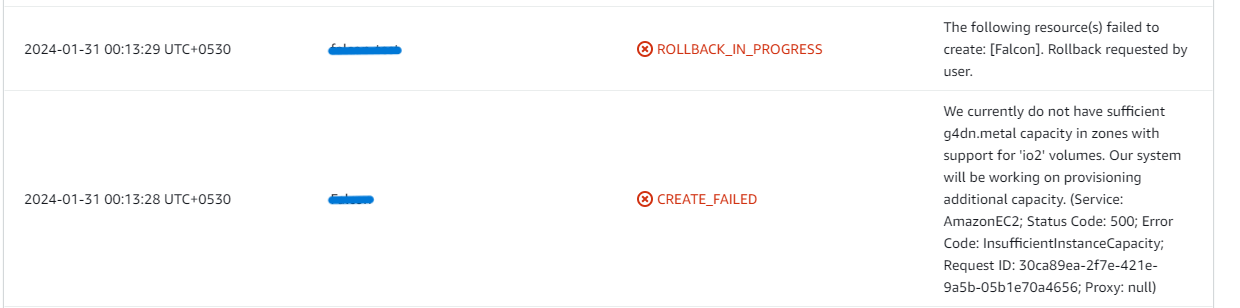
- If you face insufficient capacity errors while creating the stack, try another region or time.
- If new users never receive their confirmation or invitation emails, check the EmailHost, EmailPort, EmailHostUser and EmailHostPassword values, then look for SMTP errors in /var/log/zulip/errors.log.
Check whether the instance storage is full - uploaded files and message history grow steadily on an active Zulip server.
- Log into the server and run:
df -h
- If the root volume is between 90-100%, resize the EBS volume (per AWS docs), then reboot and restart the service.
Conclusion
The Meetrix Zulip Deployment Guide helps you bring a self-hosted, topic-based team chat into your AWS environment. Whether you're a DevOps engineer, team lead, or IT administrator, this guide gives you step-by-step instructions for a secure and reliable setup. For other self-hosted tools on AWS, see our Rocket.Chat developer guide, our Zammad help desk guide, or the roundup of collaboration tools on AWS Marketplace.
Technical Support
Reach out to Meetrix Support (aws@meetrix.io) for assistance with Zulip issues.
For questions about Zulip itself rather than the AWS deployment, the Zulip server documentation, the Zulip GitHub repository, and zulip.com are the best starting points.
Frequently Asked Questions
What is Zulip?
Zulip is an open-source team chat application. Its conversations are organized into channels and topics, so each discussion stays in its own thread and people can catch up on what matters to them without scrolling through one long stream of messages.
What are the prerequisites for installing Zulip on AWS?
You need basic knowledge of AWS services (EC2, CloudFormation), an active AWS account with appropriate permissions, a sufficient vCPU limit to launch the required instance type, and SMTP credentials so Zulip can send invitation and sign-up emails.
Which instance type is recommended?
t3a.small is a workable baseline for a small team. Move up to t3a.medium or larger as your user count and message history grow.
Why does my Zulip URL say "No organization found"?
A fresh Zulip server has no organization yet, and it will not let anyone create one without a secure link. SSH into the instance, run the generate_realm_creation_link command, and open the link it prints to create your first organization.
Why do I need to provide SMTP settings?
Zulip sends email for account confirmation, invitations, and password resets. Without working SMTP settings, new users cannot finish signing up. If you use Gmail, create an app password for the EmailHostPassword field instead of using your normal account password.
What if the automatic SSL setup fails?
Zulip tries to provision SSL automatically when the domain is hosted on Route53. If that fails, SSH into the instance and run Zulip's setup-certbot script manually - see the Generate SSL Manually section.
How do I get technical support?
Reach out to Meetrix Support at aws@meetrix.io for assistance with Zulip issues.
Ready to Deploy Your Own Zulip Server?
Get started in minutes with our pre-configured AMI and give your team threaded, topic-based chat on infrastructure you control.
Deploy Zulip from AWS Marketplace