Learn how to install and configure Zammad on AWS with our step-by-step deployment guide. This comprehensive resource walks you through provisioning your cloud environment, securely deploying Zammad, and operating it reliably in a self-hosted AWS environment. Whether you're consolidating support tickets from email and chat, building a searchable knowledge base, or replacing a hosted help desk subscription, this guide will help you set up and run Zammad efficiently in the cloud.
Zammad pairs well with the rest of a self-hosted support stack - if your team already runs a team chat tool for internal communication, Zammad handles the customer-facing side without sending ticket data to a third party. Let's get started deploying Zammad on AWS.
Prerequisites
Before you get started with the Zammad AMI, ensure you have the following prerequisites:
- Basic knowledge of AWS services, including EC2 instances and CloudFormation.
- An active AWS account with appropriate permissions.
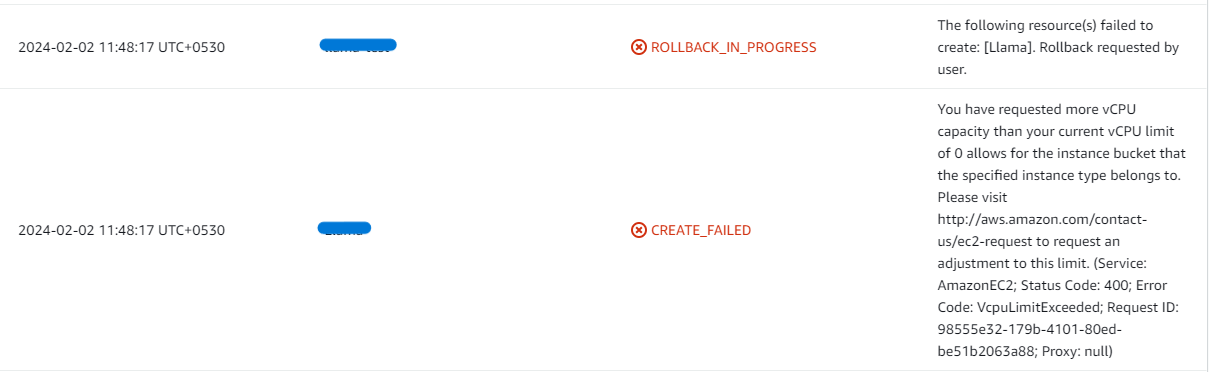
- Enough vCPU limit to create an instance (Follow https://meetrix.io/blogs/increase-aws-vcpu-quota/).
Launching the AMI
Step 1: Find and Select the Zammad AMI
- Log in to your AWS Management Console.
- Navigate to 'Zammad' in AWS Marketplace.
Step 2: Initial Setup & Configuration
- Click the "Continue to Subscribe" button.
- After subscribing, accept the terms and click "Accept Terms".
- Wait a few minutes until processing completes, then click "Continue to Configuration".
- Select "CloudFormation script to deploy Zammad" as the fulfillment option and choose your region. Click "Continue to Launch".
- From the "Choose Action" dropdown, select "Launch CloudFormation" and click "Launch".
Create CloudFormation Stack
Step 1: Create a stack
- Ensure the "Template is ready" option is selected under "Prepare template".
- Click "Next".
Step 2: Specify stack options
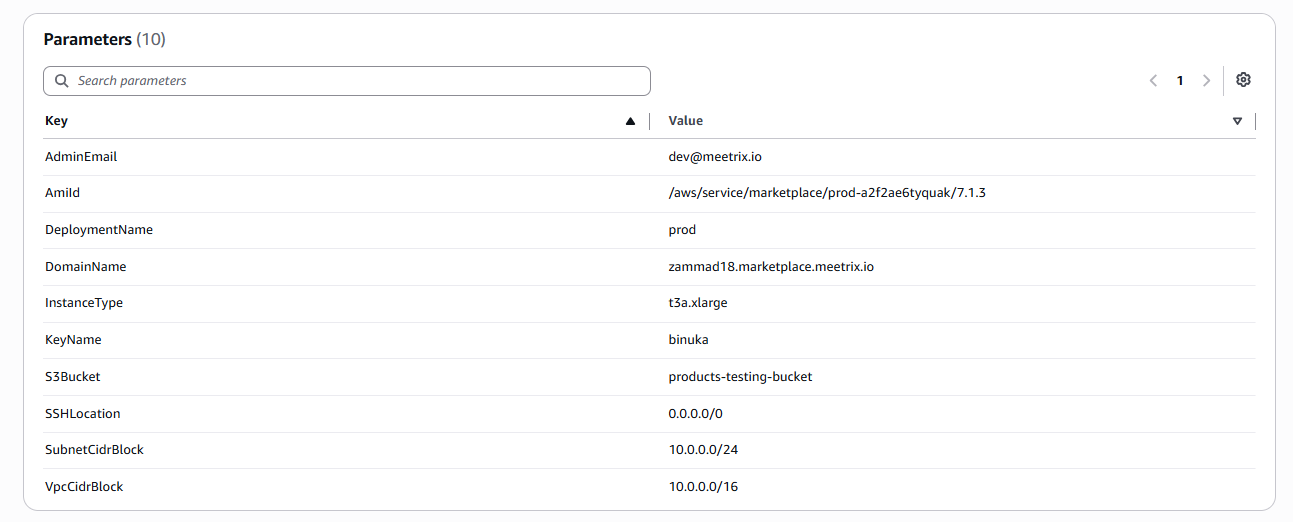
- Provide a unique "Stack name".
- Enter the "AdminEmail" used for SSL certificate generation.
- Enter a value for "DeploymentName".
- Provide a public domain for "DomainName". Zammad will automatically try to set up SSL if the domain is hosted on Route53. If unsuccessful, you must set up SSL manually.
- Choose an instance type "InstanceType" (Recommended: t3a.xlarge, since Zammad's Elasticsearch and Redis services need more headroom than a single-service AMI).
- Select your preferred "KeyName".
- Provide an S3 bucket name for "S3Bucket", used for storing PostgreSQL database backups.
- Set "SSHLocation" to 0.0.0.0/0.
- Keep "SubnetCidrBlock" as 10.0.0.0/24.
- Keep "VpcCidrBlock" as 10.0.0.0/16.
- Click "Next".
Step 3: Configure stack options
- Choose "Roll back all stack resources" and "Delete all newly created resources" under "Stack failure options".
- Click "Next".
Step 4: Review
Review and verify the details you've entered. Here's an example of a completed set of stack parameters:
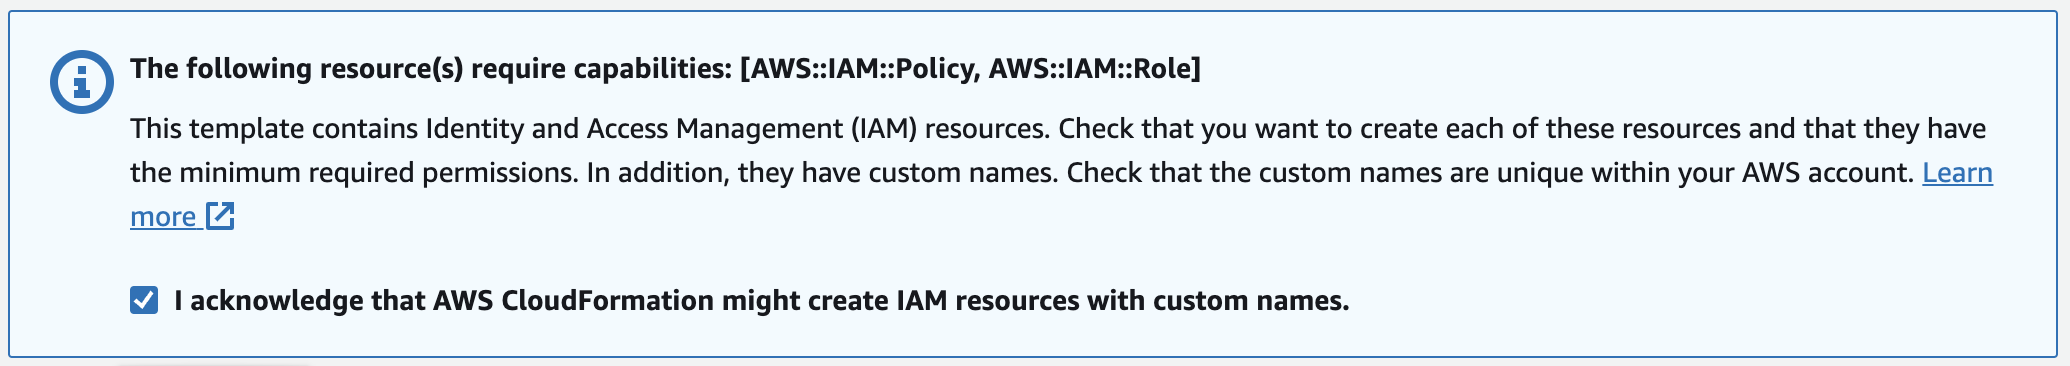
- Tick "I acknowledge that AWS CloudFormation might create IAM resources with custom names".
- Click "Submit".
Afterward, you'll be directed to the CloudFormation stacks page. Please wait for 5-10 minutes until the stack has been successfully created.
Update DNS
Step 1: Copy IP Address
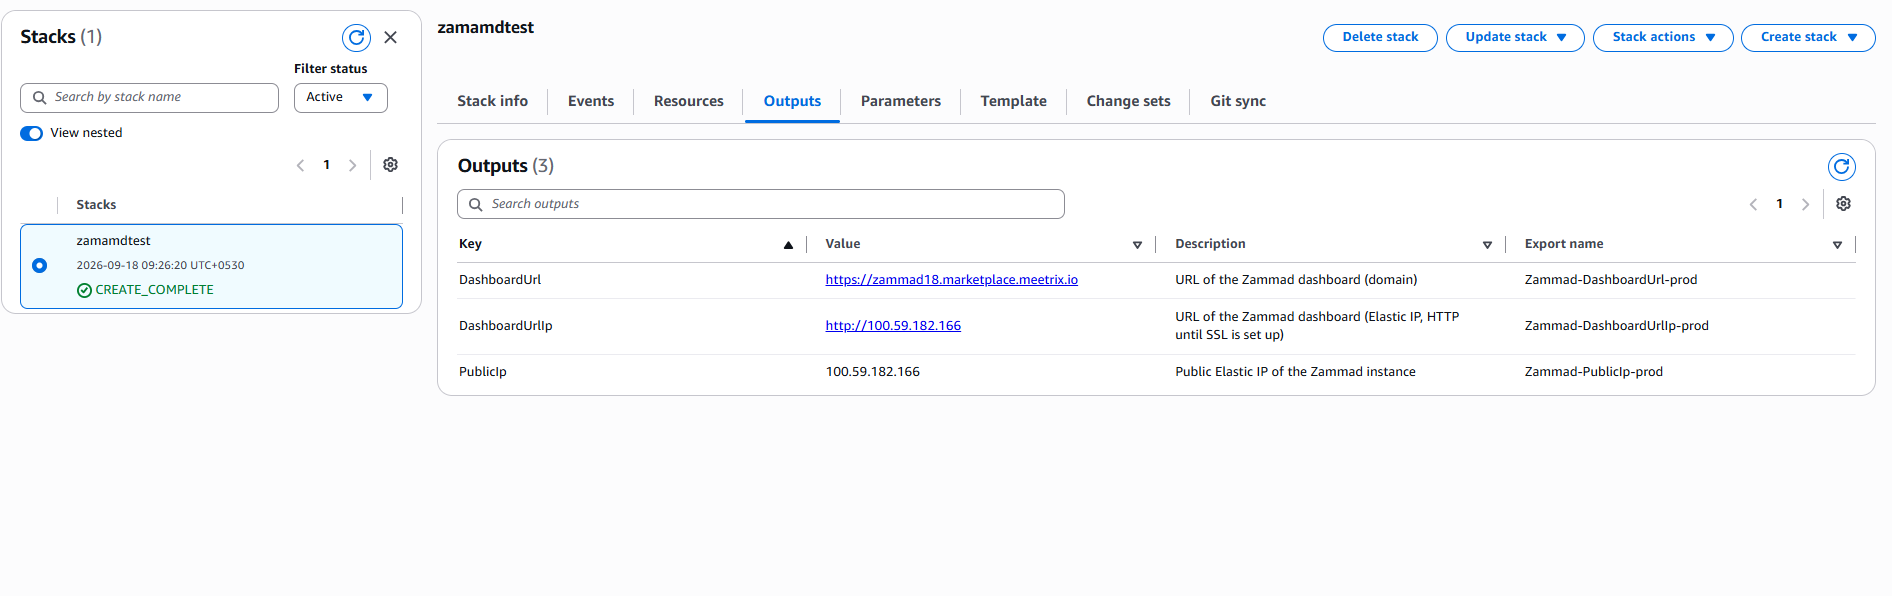
Copy the public IP labeled "PublicIp" in the "Outputs" tab.
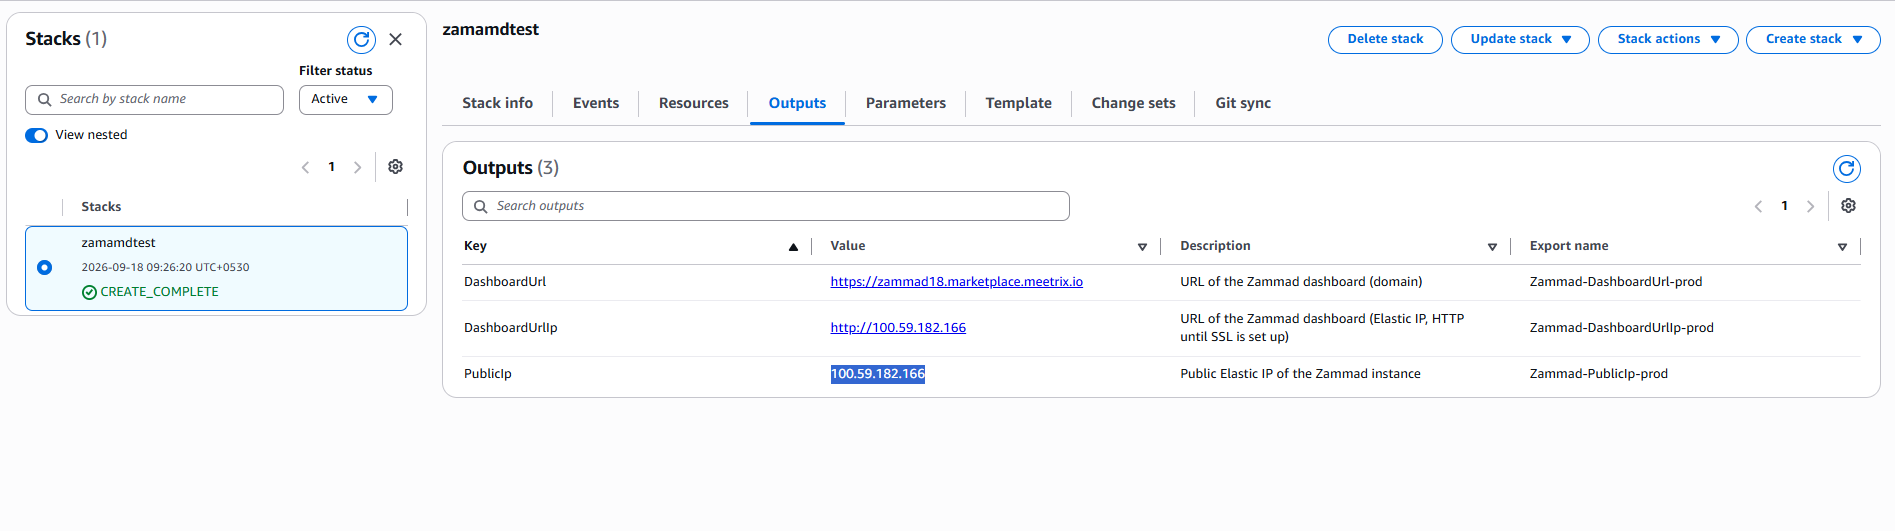
Step 2: Update DNS
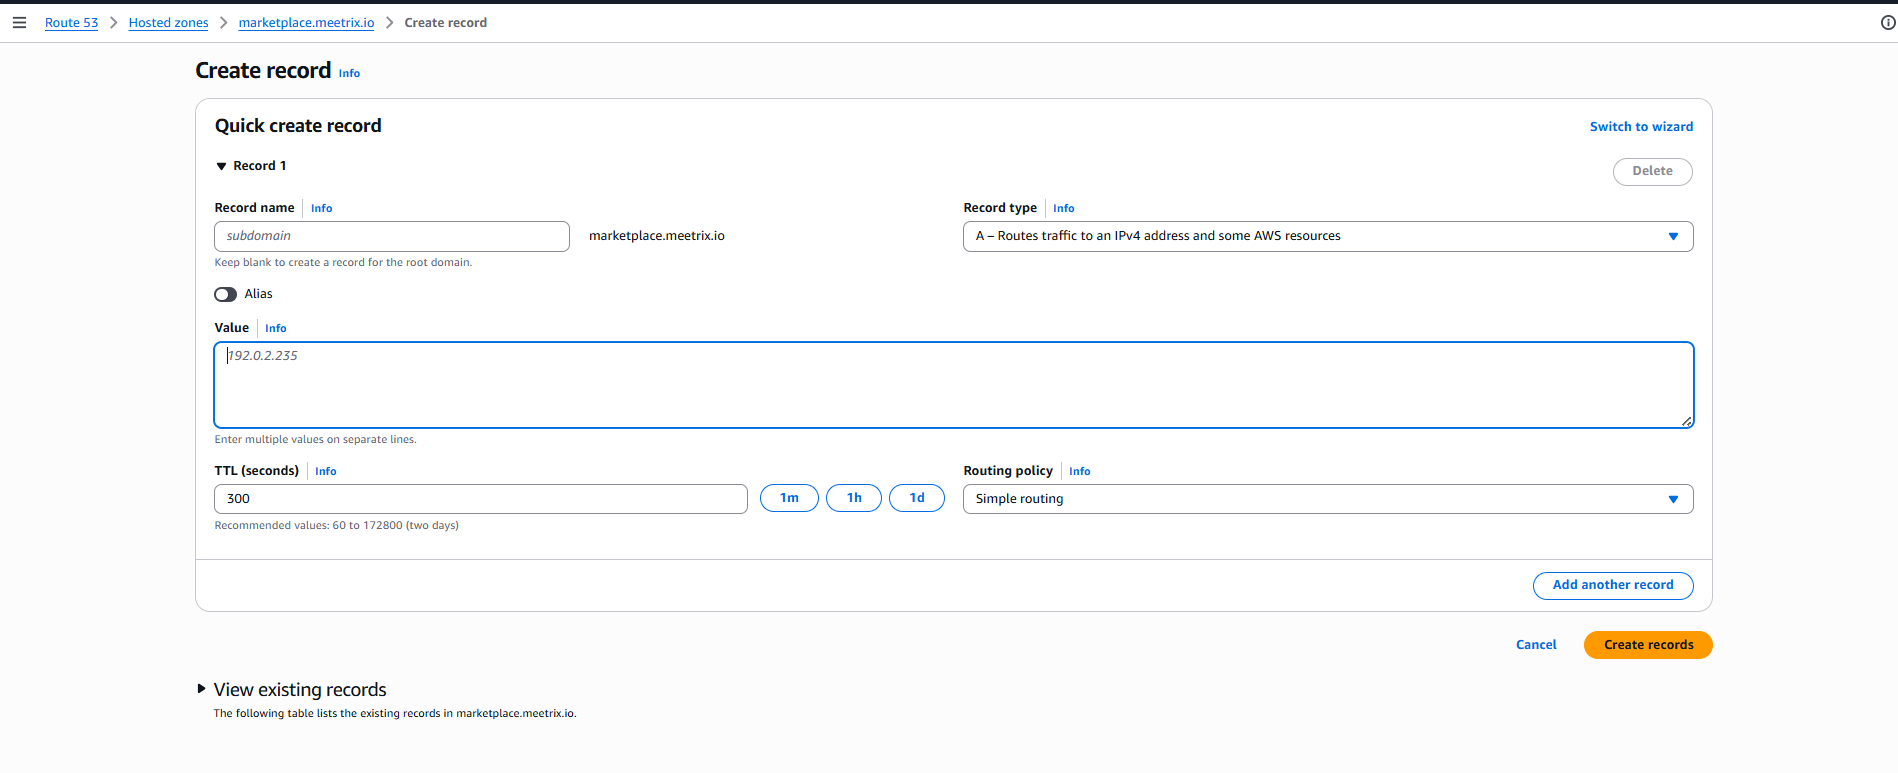
- Go to AWS Route 53 and navigate to "Hosted Zones".
- Click Create record.
- Add a record name and paste the copied PublicIp into the value textbox.
- Click "Save".
Access Zammad
Access Zammad using the "DashboardUrl" or "DashboardUrlIp" provided in the Outputs tab.
Note
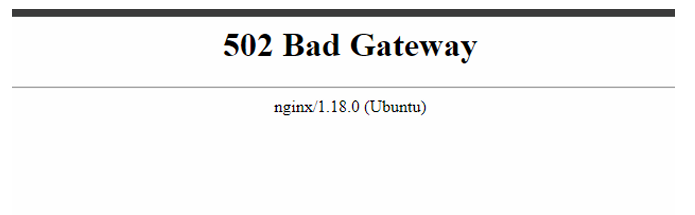
On first access, Zammad walks you through its onboarding wizard instead of a plain login form.
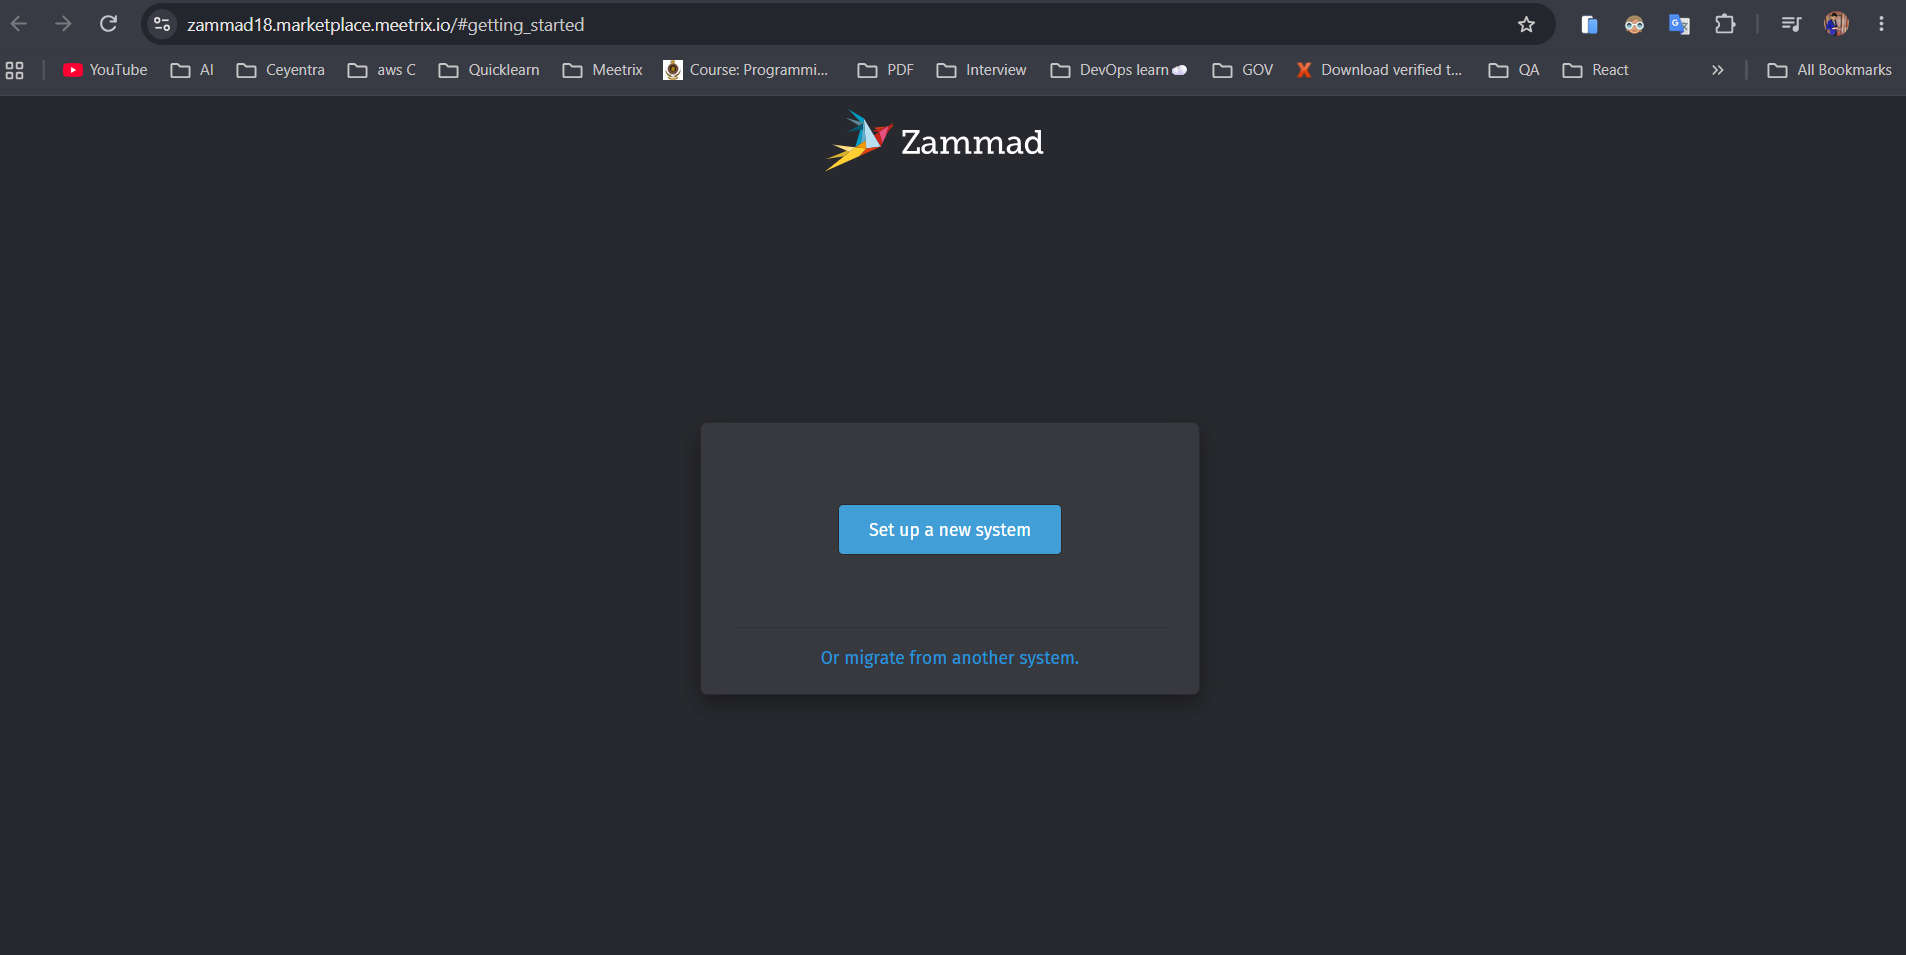
Click "Set up a new system" to create your admin account and complete the initial configuration. If your team already runs a centralized identity provider, Zammad also supports SAML and OAuth2 login - see our Authentik developer guide if you want to put Zammad behind the same SSO your other self-hosted tools use.
Generate SSL Manually
Zammad will automatically try to set up SSL when a Route53-hosted domain is provided. If it fails, follow these steps to generate SSL manually.
Step 1: Copy IP Address
Follow the Update DNS steps above, if not already done, and copy the Public IP indicated as "PublicIp" in the "Outputs" tab.
Step 2: Log in to the server
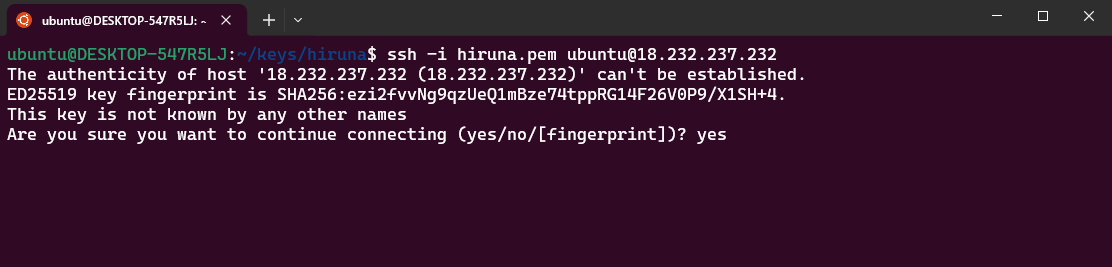
- Open the terminal and go to the directory where your private key is located.
- Run: ssh -i <your key name> ubuntu@<Public IP address>
- Type "yes" and press Enter to confirm.
Step 3: Generate SSL
Run the following command and follow the prompts:
sudo /root/certificate_generate_standalone.shCheck Server Logs
Step 1: Log in to the server
ssh -i <your key name> ubuntu@<Public IP address>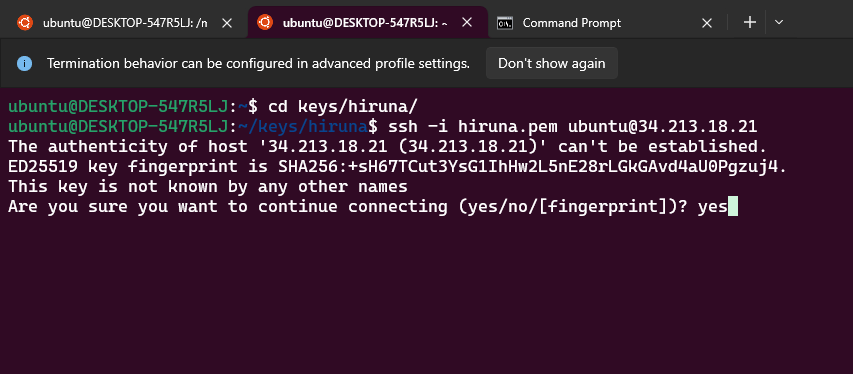
Step 2: Check the logs
sudo docker ps

sudo docker logs <container-id-prefix>
Shutting Down Zammad
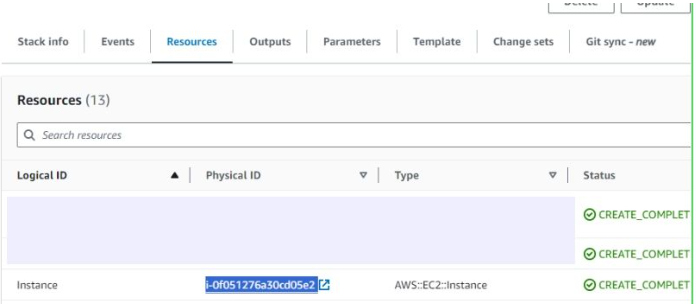
- In CloudFormation, click the link labeled "Instance" in the "Resources" tab to open the EC2 instance.
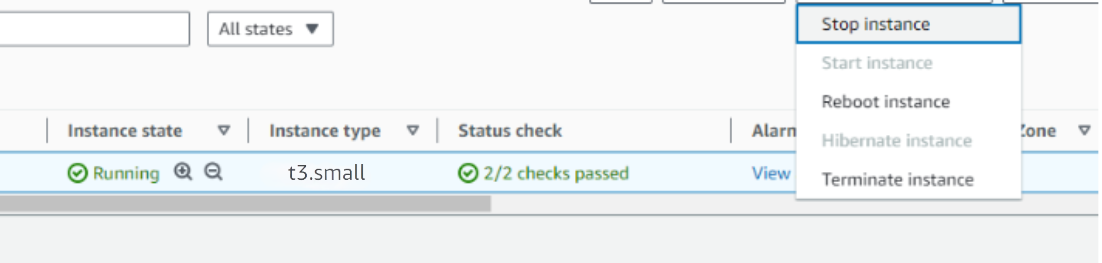
- Stop the Zammad instance from the Instance state dropdown. You can restart it later as needed.
Remove Zammad
Delete the CloudFormation stack from the AWS Management Console under "CloudFormation Stacks" by clicking "Delete".
Upgrades
When a new version is available in AWS Marketplace, remove the previous deployment after backing up necessary server data, and relaunch with the new version.
Troubleshoot
- If you face vCPU quota limits, request an increase: How to increase AWS quota.
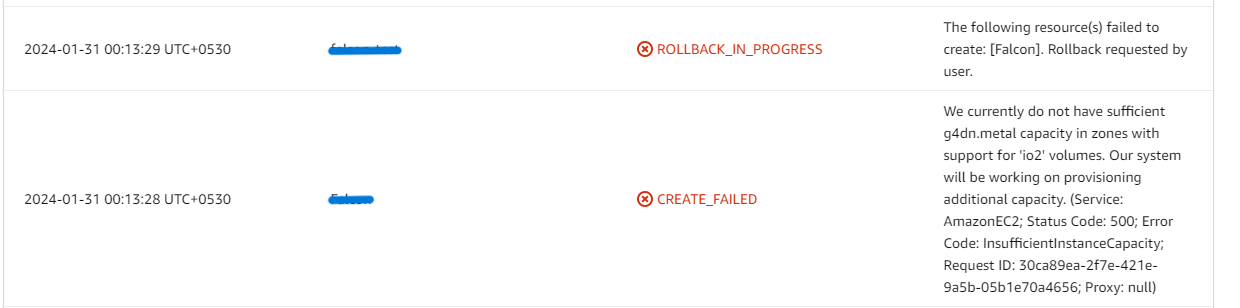
- If you face insufficient capacity errors while creating the stack, try another region or time.
Check whether the instance storage is full - Zammad's Elasticsearch index can grow quickly on busy support desks.
- Log into the server and run:
df -h
- If the root volume is between 90-100%, resize the EBS volume (per AWS docs), then reboot and restart the service.
Conclusion
The Meetrix Zammad Deployment Guide helps you integrate a self-hosted help desk into your AWS environment. Whether you're a DevOps engineer, support lead, or IT administrator, this guide provides step-by-step instructions for a secure and reliable setup. For a broader look at self-hosting business software on AWS, see our ERPNext developer guide or our roundup of collaboration tools on AWS Marketplace.
Technical Support
Reach out to Meetrix Support (aws@meetrix.io) for assistance with Zammad issues.
For questions about Zammad itself rather than the AWS deployment, the official Zammad documentation, the Zammad GitHub repository, and zammad.com are the best starting points.
Frequently Asked Questions
What is Zammad?
Zammad is an open-source help desk and customer support ticketing system. It brings email, chat, phone, and social media requests into a single queue, and adds a knowledge base, SLA tracking, and reporting on top.
What are the prerequisites for installing Zammad on AWS?
You need basic knowledge of AWS services (EC2, CloudFormation), an active AWS account with appropriate permissions, and a sufficient vCPU limit to launch the required instance type.
Which instance type is recommended, and why?
t3a.xlarge is recommended as a baseline. Zammad's stack bundles PostgreSQL, Redis, and Elasticsearch alongside the Rails application, so it needs more memory and CPU headroom than a typical single-service AMI.
What is the S3Bucket parameter used for?
It points the instance at an S3 bucket in your own account for storing PostgreSQL database backups. You can leave the default if you don't need automated backups yet.
What if the automatic SSL setup fails?
Zammad tries to provision SSL automatically when the domain is hosted on Route53. If that fails, SSH into the instance and run the certificate script manually - see the Generate SSL Manually section below.
How do I handle upgrades?
When a new version is available in the AWS Marketplace, back up your data, remove the previous deployment, then relaunch with the new version.
How do I get technical support?
Reach out to Meetrix Support at aws@meetrix.io for assistance with Zammad issues.
Ready to Deploy Your Own Zammad Instance?
Get started in minutes with our pre-configured AMI and bring your support tickets, knowledge base, and SLAs into a self-hosted help desk you control.
Deploy Zammad from AWS Marketplace